

[Sep 15, 2026] Get New 300-715 Practice Test Questions Answers
300-715 Dumps and Exam Test Engine
To pass the Cisco 300-715 exam, candidates must have a solid understanding of the concepts and technologies related to network access control, such as IEEE 802.1X authentication, MAC Authentication Bypass (MAB), and Network Admission Control (NAC). They must also have experience configuring ISE features, such as authentication and authorization policies, profiling, posture assessment, and guest access.
NEW QUESTION # 184
An engineer is working on a switch and must tag packets with SGT values such that it learns via SXP. Which command must be entered to meet this requirement?
- A. ip device tracking maximum
- B. ip arp inspection
- C. ip source guard
- D. ip dhcp snooping
Answer: D
NEW QUESTION # 185
Which two actions occur when a Cisco ISE server device administrator logs in to a device? (Choose two)
- A. The Cisco ISE server queries the internal identity store
- B. The device queries the external identity store
- C. The device queries the Cisco ISE authorization server
- D. The device queries the internal identity store
- E. The Cisco ISE server queries the external identity store.
Answer: C,E
NEW QUESTION # 186
Which three conditions can be used for posture checking? (Choose three.)
- A. certificate
- B. services
- C. operating system
- D. file
- E. application
Answer: B,D,E
NEW QUESTION # 187
An administrator needs to give the same level of access to the network devices when users are logging into them using TACACS+ However, the administrator must restrict certain commands based on one of three user roles that require different commands How is this accomplished without creating too many objects using Cisco ISE?
- A. Create one shell profile and multiple command sets.
- B. Create multiple shell profiles and multiple command sets.
- C. Create one shell profile and one command set.
- D. Create multiple shell profiles and one command set
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-1/admin_guide/b_ise_admin_guide_21/b_ise_admin_guide_20_chapter_0100010.html
https://www.youtube.com/watch?v=IlZwB71Szog&ab_channel=JasonMaynard
NEW QUESTION # 188
An organization wants to split their Cisco ISE deployment to separate the device administration functionalities from the mam deployment. For this to work, the administrator must deregister any nodes that will become a part of the new deployment, but the button for this option is grayed out.
Which configuration is causing this behavior?
- A. One of the nodes is the Primary PAN
- B. All of the nodes are actively being synched.
- C. One of the nodes is an active PSN.
- D. All of the nodes participate in the PAN auto failover.
Answer: A
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-
4/admin_guide/b_ISE_admin_guide_24/m_setup_cisco_ise.html#ID185
NEW QUESTION # 189
Drag and drop the description from the left onto the protocol on the right that is used to carry out system authentication, authentication, and accounting.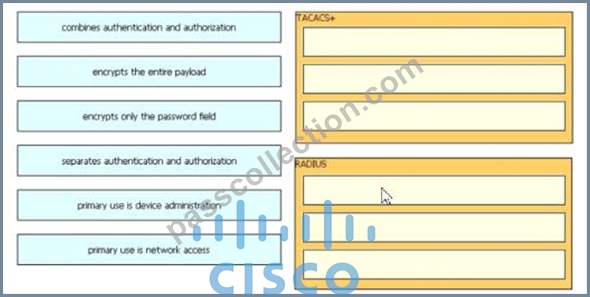
Answer:
Explanation: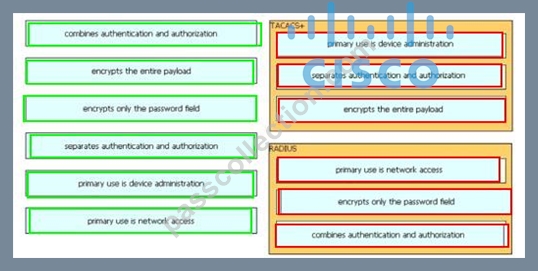
NEW QUESTION # 190
Which platform does a Windows-based device download the Network Assistant from?
- A. Microsoft app store
- B. Cisco download site
- C. native OS
- D. Cisco ISE
Answer: D
NEW QUESTION # 191
A user is attempting to register a BYOD device to the Cisco ISE deployment, but needs to use the onboarding policy to request a digital certificate and provision the endpoint.
What must be configured to accomplish this task?
- A. The BYOD flow to ensure that the endpoint will be provisioned prior to registering
- B. The Cisco AnyConnect provisioning policy to provision the endpoint for onboarding
- C. The posture provisioning policy to give the endpoint all necessary components prior to registering
- D. A native supplicant provisioning policy to redirect them to the BYOD portal for onboarding
Answer: D
NEW QUESTION # 192
An engineer is configuring 802.1X and wants it to be transparent from the users' point of view.
The implementation should provide open authentication on the switch ports while providing strong levels of security for non-authenticated devices. Which deployment mode should be used to achieve this?
- A. closed
- B. open
- C. low-impact
- D. high-impact
Answer: C
Explanation:
1. Remember that the goal of low-impact mode is to provide very limited network access to devices without authentication and then provide very specific access to those that have been authorized; this is the least privilege security principle.
2. Low-impact mode uses authentication open but adds security on top of the framework was built in monitor mode. It uses a PACL on the switch port to permit critical traffic of certain endpoints, such as thin clients, to function prior to an attempted authentication. After the authentication, the authorization should provide specific access, unlike monitor mode, which is the same before and after authentication.
NEW QUESTION # 193
A client with MAC address 04:77:10:14:67:AB connects to the network. The client does not support 802.1X. Which setting must be enabled in the Allowed Authentication Protocols list in your Authentication Policy for Cisco ISE Server to support MAB authentication for this MAC address?
- A. Process Host Lookup
- B. EAP-FAST
- C. EAP-TTLS
- D. MS-CHAPv2
Answer: A
NEW QUESTION # 194
Which two components are required for creating a Native Supplicant Profile within a BYOD flow? (Choose two )
- A. Connection Type
- B. iOS Settings
- C. Redirect ACL
- D. Windows Settings
- E. Operating System
Answer: B,E
NEW QUESTION # 195
An administrator needs to connect ISE to Active Directory as an external authentication source and allow the proper ports through the firewall. Which two ports should be opened to accomplish this task? (Choose two)
- A. HTTPS 443
- B. TELNET 23
- C. MSRPC 445
- D. LDAP 389
- E. HTTP 80
Answer: C,D
NEW QUESTION # 196
An administrator is migrating device administration access to Cisco ISE from the legacy TACACS+ solution that used only privilege 1 and 15 access levels. The organization requires more granular controls of the privileges and wants to customize access levels 2-5 to correspond with different roles and access needs. Besides defining a new shell profile in Cisco ISE.
What must be done to accomplish this configuration?
- A. Enable the privilege levels in the IOS devices
- B. Define the command privileges for levels 2-5 in the IOS devices
- C. Define the command privileges for levels 2-5 in Cisco ISE
- D. Enable the privilege levels in Cisco ISE
Answer: C
Explanation:
The command privileges for 2 - 5 are defined in ISE, not on the IOS device. If the IOS device defines the command privileges, then why do we even need ISE. When ISE is centrally managing the network devices, it configures the command privileges and the shell profile.
NEW QUESTION # 197
What are two differences between the RADIUS and TACACS+ protocols'? (Choose two.)
- A. TACACS+uses TCP port 49. whereas RADIUS uses UDP ports 1812 and 1813.
- B. RADIUS is a Cisco proprietary protocol, whereas TACACS+ is an open standard protocol
- C. RADIUS combines authentication and authorization, whereas TACACS+ does not
- D. RADIUS enables encryption of all the packets, whereas with TACACS+. only the password is encrypted.
- E. RADIUS offers multiprotocol support, whereas TACACS+ does not
Answer: A,C
NEW QUESTION # 198
A network administrator changed a Cisco ISE deployment from pilot to production and noticed that the JVM memory utilization increased significantly. The administrator suspects this is due to replication between the nodes What must be configured to minimize performance degradation?
- A. Enable the endpoint attribute filter
- B. Ensure that Cisco ISE is updated with the latest profiler feed update
- C. Change the reauthenticate interval.
- D. Review the profiling policies for any misconfiguration
Answer: A
Explanation:
Explanation
https://www.cisco.com/c/en/us/td/docs/security/ise/2-3/admin_guide/b_ise_admin_guide_23/b_ise_admin_guide
NEW QUESTION # 199
When setting up profiling in an environment using Cisco ISE for network access control, an organization must use non-proprietary protocols for collecting the information at layer 2. Which two probes will provide this information without forwarding SPAN packets to Cisco ISE? {Choose two.)
- A. DNS probe
- B. RADIUS probe
- C. NetFlow probe
- D. DHCP SPAN probe
- E. SNMP query probe
Answer: B,E
Explanation:
Explanation
https://ciscocustomer.lookbookhq.com/iseguidedjourney/ISE-profiling-design
NEW QUESTION # 200 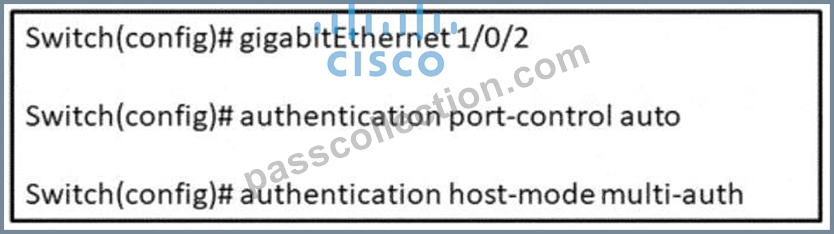
Refer to the exhibit. In which scenario does this switch configuration apply?
- A. when passing IP phone authentication
- B. when allowing multiple IP phones to be connected
- C. when allowing a hub with multiple clients connected
- D. when preventing users with hypervisor
Answer: C
Explanation:
https://www.linkedin.com/pulse/mac-authentication-bypass-priyanka-kumari#:~:text=Multi%
2Dauthentication%20host%20mode%3A%20You,allows%20multiple%20source%20MAC%20addresses.
NEW QUESTION # 201
A network administrator has just added a front desk receptionist account to the Cisco ISE Guest Service sponsor group.
Using the Cisco ISE Guest Sponsor Portal, which guest services can the receptionist provide?
- A. Configure authorization settings for guest users
- B. Keep track of guest user activities
- C. Authenticate guest users to Cisco ISE
- D. Create and manage guest user accounts
Answer: D
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-
1/sponsor_guide/b_spons_SponsorPortalUserGuide_21/Support_Guests.html
NEW QUESTION # 202
......
2026 New PassCollection 300-715 PDF Recently Updated Questions: https://www.passcollection.com/300-715_real-exams.html
Cisco 300-715 DUMPS WITH REAL EXAM QUESTIONS: https://drive.google.com/open?id=1XQJ6Rdt323YhncYz_UVuEisJ_inUVbbV
