

300-715 Practice Exam and Study Guides - Verified By PassCollection Updated 153 Questions
2022 Updated Verified Pass 300-715 Study Guides & Best Courses
NEW QUESTION 75
Which three default endpoint identity groups does Cisco ISE create? (Choose three.)
- A. allow list
- B. block list
- C. unknown
- D. endpoint
- E. profiled
Answer: B,C,E
Explanation:
Section: Profiler
Explanation
Explanation/Reference: https://www.cisco.com/en/US/docs/security/ise/1.0/user_guide/ ise10_man_identities.html#wp1203054
NEW QUESTION 76
An engineer is configuring Cisco ISE and needs to dynamically identify the network endpoints and ensure that endpoint access is protected. Which service should be used to accomplish this task?
- A. Guest access
- B. Profiling
- C. Posture
- D. Client provisioning
Answer: B
NEW QUESTION 77
An engineer is designing a BYOD environment utilizing Cisco ISE for devices that do not support native supplicants Which portal must the security engineer configure to accomplish this task?
- A. MDM
- B. My devices
- C. BYOD
- D. Client provisioning
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-2/admin_guide/b_ise_admin_guide_22/b_ise_admin_guide_22_chapter_01111.html
NEW QUESTION 78
What is the minimum certainty factor when creating a profiler policy?
- A. the maximum number that a device certainty factor must reach to become a member of the profile
- B. the maximum number that a predefined condition provides
- C. the minimum number that a device certainty factor must reach to become a member of the profile
- D. the minimum number that a predefined condition provides
Answer: B
NEW QUESTION 79
A Cisco ISE server sends a CoA to a NAD after a user logs in successfully using CWA Which action does the CoA perform?
- A. It triggers the NAD to reauthenticate the client
- B. It applies new permissions provided in the CoA to the client session.
- C. It applies the downloadable ACL provided in the CoA
- D. It terminates the client session
Answer: C
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/115732-central-web-auth-00.html
https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/113362-config-web-auth-ise-00.html
NEW QUESTION 80
Drag the descriptions on the left onto the components of 802.1X on the right.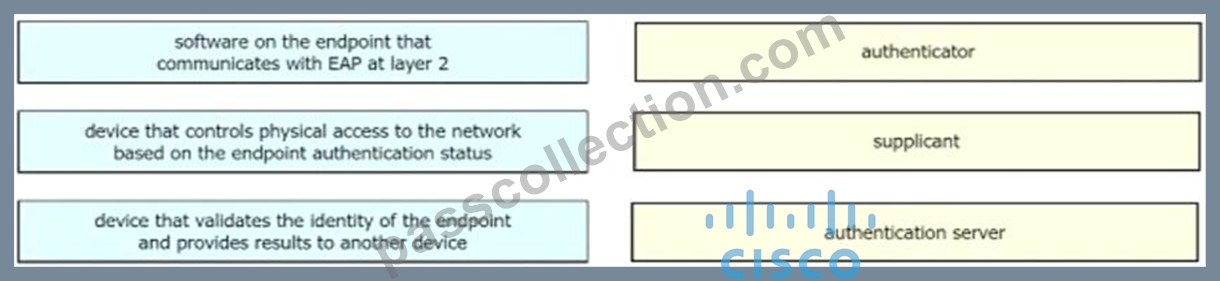
Answer:
Explanation: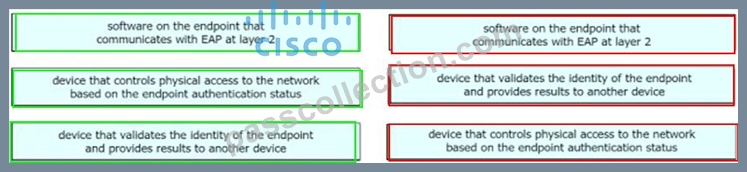
NEW QUESTION 81
When planning for the deployment of Cisco ISE, an organization's security policy dictates that they must use network access authentication via RADIUS. It also states that the deployment needs to provide an adequate amount of security and visibility for the hosts on the network.
Why should the engineer configure MAB in this situation?
- A. MAB provides the strongest form of authentication available.
- B. The Cisco switches only support MAB.
- C. MAB provides user authentication.
- D. The devices in the network do not have a supplicant.
Answer: D
Explanation:
Section: Endpoint Compliance
NEW QUESTION 82
Which two probes must be enabled for the ARP cache to function in the Cisco ISE profile service so that a user can reliably bind the IP address and MAC addresses of endpoints? (Choose two.)
- A. DHCP
- B. RADIUS
- C. NetFlow
- D. SNMP
- E. HTTP
Answer: A,B
Explanation:
Cisco ISE implements an ARP cache in the profiling service, so that you can reliably map the IP addresses and the MAC addresses of endpoints. For the ARP cache to function, you must enable either the DHCP probe or the RADIUS probe. The DHCP and RADIUS probes carry the IP addresses and the MAC addresses of endpoints in the payload data. The dhcp-requested address attribute in the DHCP probe and the Framed-IP-address attribute in the RADIUS probe carry the IP addresses of endpoints, along with their MAC addresses, which can be mapped and stored in the ARP cache.
https://www.cisco.com/c/en/us/td/docs/security/ise/2-
1/admin_guide/b_ise_admin_guide_21/b_ise_admin_guide_20_chapter_010100.html
NEW QUESTION 83
Which default endpoint identity group does an endpoint that does not match any profile in Cisco ISE become a member of?
- A. Endpoint
- B. blacklist
- C. white list
- D. unknown
- E. profiled
Answer: D
Explanation:
Reference:
If you do not have a matching profiling policy, you can assign an unknown profiling policy. The endpoint is therefore profiled as Unknown. The endpoint that does not match any profile is grouped within the Unknown identity group. The endpoint profiled to the Unknown profile requires that you create a profile with an attribute or a set of attributes collected for that endpoint.
https://www.cisco.com/en/US/docs/security/ise/1.0/user_guide/ise10_man_identities.html
NEW QUESTION 84
In a standalone Cisco ISE deployment, which two personas are configured on a node? (Choose two )
- A. policy service
- B. primary
- C. publisher
- D. administration
- E. subscriber
Answer: A,D
NEW QUESTION 85
Drag and drop the description from the left onto the protocol on the right that is used to carry out system authentication, authentication, and accounting.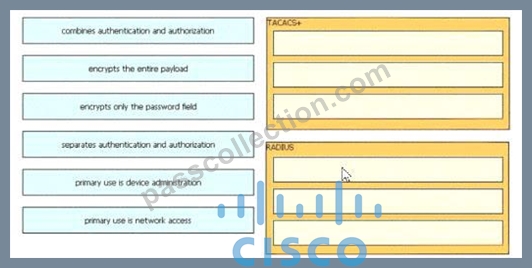
Answer:
Explanation: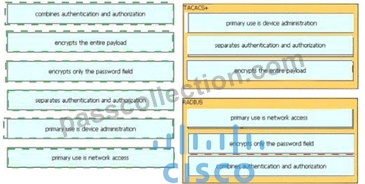
Explanation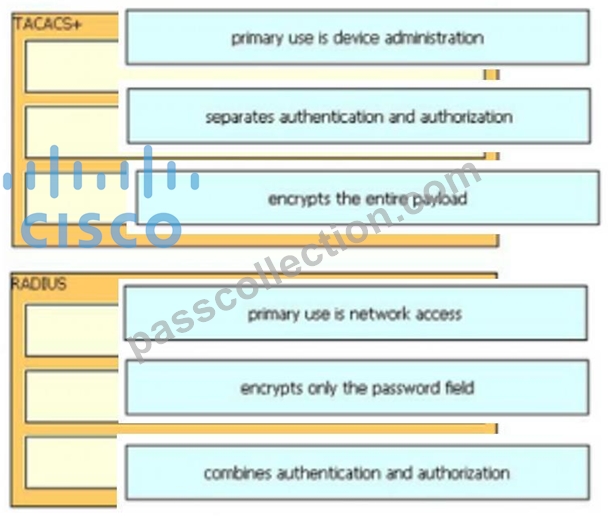
https://www.mbne.net/tech-notes/aaa-tacacs-radius
NEW QUESTION 86
What are the three default behaviors of Cisco ISE with respect to authentication, when a user connects to a switch that is configured for 802.1X, MAB, and WebAuth? (Choose three)
- A. Dot1 traffic uses internal users for retrieving identity.
- B. Unmatched traffic is allowed on the network.
- C. MAB traffic uses internal endpoints for retrieving identity.
- D. Unmatched traffic is dropped because of the Reject/Reject/Drop action that is configured under Options.
- E. Dot1X traffic uses a user-defined identity store for retrieving identity.
Answer: A,C,D
NEW QUESTION 87
Refer to the exhibit. An engineer is creating a new TACACS* command set and cannot use any show commands after togging into the device with this command set authorization Which configuration is causing this issue?
- A. Question marks are not allowed as wildcards for command sets.
- B. The command set is allowing all commands that are not in the command list
- C. The command set is working like an ACL and denying every command.
- D. The wildcard command listed is in the wrong format
Answer: A
NEW QUESTION 88
Which two values are compared by the binary comparison (unction in authentication that is based on Active Directory?
- A. subject alternative name and the common name
- B. MS-CHAPv2 provided machine credentials and credentials stored in Active Directory
- C. user-presented password hash and a hash stored in Active Directory
- D. user-presented certificate and a certificate stored in Active Directory
Answer: A,B
Explanation:
Explanation
Basic certificate checking does not require an identity source. If you want binary comparison checking for the certificates, you must select an identity source. If you select Active Directory as an identity source, subject and common name and subject alternative name (all values) can be used to look up a user.
https://www.cisco.com/c/en/us/td/docs/security/ise/1-3/admin_guide/b_ise_admin_guide_13/b_ise_admin_guide_sample_chapter_01110.html
NEW QUESTION 89
What is needed to configure wireless guest access on the network?
- A. endpoint already profiled in ISE
- B. valid user account in Active Directory
- C. WEBAUTH ACL for redirection
- D. Captive Portal Bypass turned on
Answer: C
NEW QUESTION 90
......
Ultimate Guide to the 300-715 - Latest Edition Available Now: https://www.passcollection.com/300-715_real-exams.html
2022 Updated Verified Pass 300-715 Exam - Real Questions & Answers: https://drive.google.com/open?id=1XQJ6Rdt323YhncYz_UVuEisJ_inUVbbV
