

Pass Your Kubernetes Administrator CKA Exam on Jan 02, 2024 with 68 Questions
CKA Free Exam Study Guide! (Updated 68 Questions)
NEW QUESTION # 27
Create the service as type NodePort with the port 32767 for the nginx pod with the pod selector app: my-nginx
Answer:
Explanation:
kubectl run nginx --image=nginx --restart=Never -- labels=app=nginx --port=80 --dry-run -o yaml > nginx-pod.yaml
NEW QUESTION # 28
Score: 4%
Task
Create a pod named kucc8 with a single app container for each of the following images running inside (there may be between 1 and 4 images specified): nginx + redis + memcached .
Answer:
Explanation:
Solution:
kubectl run kucc8 --image=nginx --dry-run -o yaml > kucc8.yaml
# vi kucc8.yaml
apiVersion: v1
kind: Pod
metadata:
creationTimestamp: null
name: kucc8
spec:
containers:
- image: nginx
name: nginx
- image: redis
name: redis
- image: memcached
name: memcached
- image: consul
name: consul
#
kubectl create -f kucc8.yaml
#12.07
NEW QUESTION # 29
Create a persistent volume with name app-data, of capacity 2Gi and access mode ReadWriteMany. The type of volume is hostPath and its location is /srv/app-data.
Answer:
Explanation:
See the solution below.
Explanation
solution
Persistent Volume
A persistent volume is a piece of storage in a Kubernetes cluster. PersistentVolumes are a cluster-level resource like nodes, which don't belong to any namespace. It is provisioned by the administrator and has a particular file size. This way, a developer deploying their app on Kubernetes need not know the underlying infrastructure. When the developer needs a certain amount of persistent storage for their application, the system administrator configures the cluster so that they consume the PersistentVolume provisioned in an easy way.
Creating Persistent Volume
kind: PersistentVolumeapiVersion: v1metadata: name:app-dataspec: capacity: # defines the capacity of PV we are creating storage: 2Gi #the amount of storage we are tying to claim accessModes: # defines the rights of the volume we are creating - ReadWriteMany hostPath: path: "/srv/app-data" # path to which we are creating the volume Challenge
* Create a Persistent Volume named ReadWriteMany, storage classname
shared, 2Gi of storage capacity and the host path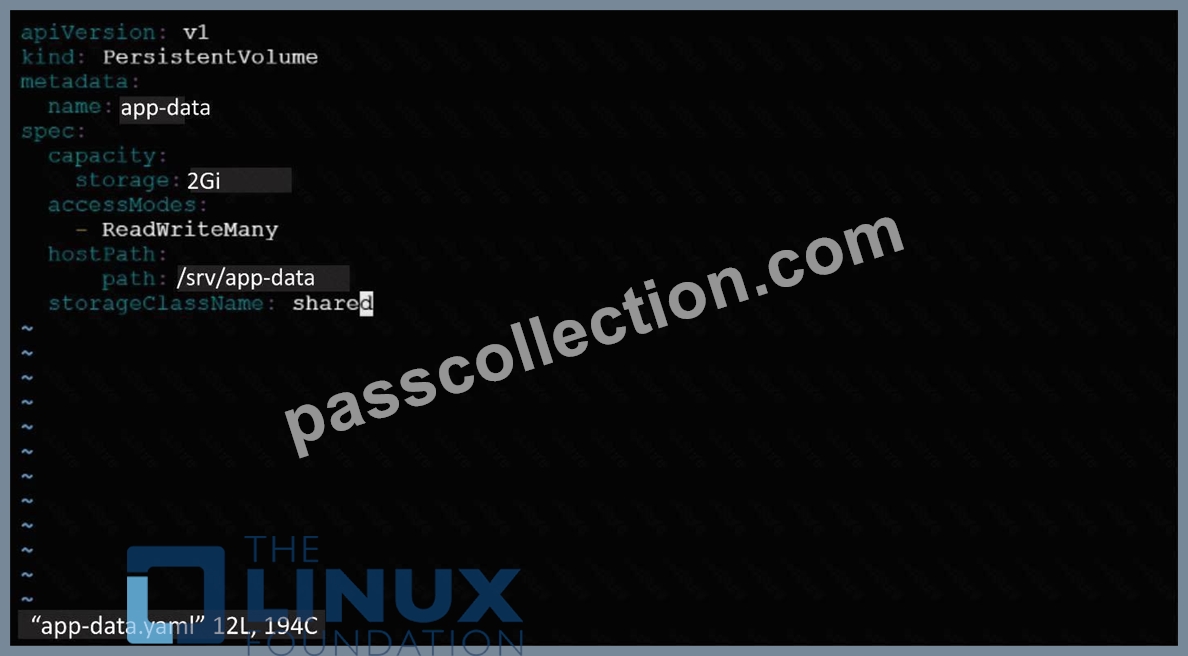
2. Save the file and create the persistent volume.
Image for post
3. View the persistent volume.
* Our persistent volume status is available meaning it is available and it has not been mounted yet. This status will change when we mount the persistentVolume to a persistentVolumeClaim.
PersistentVolumeClaim
In a real ecosystem, a system admin will create the PersistentVolume then a developer will create a PersistentVolumeClaim which will be referenced in a pod. A PersistentVolumeClaim is created by specifying the minimum size and the access mode they require from the persistentVolume.
Challenge
* Create a Persistent Volume Claim that requests the Persistent Volume we had created above. The claim should request 2Gi. Ensure that the Persistent Volume Claim has the same storageClassName as the persistentVolume you had previously created.
kind: PersistentVolumeapiVersion: v1metadata: name:
spec:
accessModes: - ReadWriteMany
requests: storage: 2Gi
storageClassName: shared
2. Save and create the pvc
njerry191@cloudshell:~ (extreme-clone-2654111)$ kubect1 create -f app-data.yaml persistentvolumeclaim/app-data created
3. View the pvc
Image for post
4. Let's see what has changed in the pv we had initially created.
Image for post
Our status has now changed from available to bound.
5. Create a new pod named myapp with image nginx that will be used to Mount the Persistent Volume Claim with the path /var/app/config.
Mounting a Claim
apiVersion: v1kind: Podmetadata: creationTimestamp: null name: app-dataspec: volumes: - name:congigpvc persistenVolumeClaim: claimName: app-data containers: - image: nginx name: app volumeMounts: - mountPath: "/srv/app-data " name: configpvc
NEW QUESTION # 30
Change the label for one of the pod to env=uat and list all the pods to verify
Answer:
Explanation:
kubectl label pod/nginx-dev3 env=uat --overwrite kubectl get pods --show-labels
NEW QUESTION # 31
Update the deployment with the image version 1.17.4 and verify
- A. kubectl set image deploy/webapp nginx=nginx:1.17.4
//Verify
kubectl describe deploy webapp | grep Image
kubectl get deploy -o=jsonpath='{range.items [*]}{.[*]}
{.metadata.name}{"\t"}{.spec.template.spec.containers[*].i
mage}{"\n"}' - B. kubectl set image deploy/webapp nginx=nginx:1.17.4
//Verify
kubectl describe deploy webapp | grep Image
kubectl get deploy -
{.metadata.name}{"\t"}{.spec.template.spec.containers[*].i
mage}{"\n"}'
Answer: A
NEW QUESTION # 32
For this item, you will have to ssh to the nodes ik8s-master-0 and ik8s-node-0 and complete all tasks on these nodes. Ensure that you return to the base node (hostname: node-1) when you have completed this item.
Context
As an administrator of a small development team, you have been asked to set up a Kubernetes cluster to test the viability of a new application.
Task
You must use kubeadm to perform this task. Any kubeadm invocations will require the use of the
--ignore-preflight-errors=all option.
* Configure the node ik8s-master-O as a master node. .
* Join the node ik8s-node-o to the cluster.
Answer:
Explanation:
See the solution below.
Explanation
solution
You must use the kubeadm configuration file located at /etc/kubeadm.conf when initializingyour cluster.
You may use any CNI plugin to complete this task, but if you don't have your favourite CNI plugin's manifest URL at hand, Calico is one popular option: https://docs.projectcalico.org/v3.14/manifests/calico.yaml Docker is already installed on both nodes and has been configured so that you can install the required tools.
NEW QUESTION # 33
Remove taint added to node "worker-2"
Answer:
Explanation:
kubectl taint nodes worker-2 key:NoSchedule- // Verify You will see a message "node/worker-2 untainted" kubectl get nodes -o customcolumns=NAME:.metadata.name,TAINTS:.spec.taints --no-headers
NEW QUESTION # 34
Get list of all the pods showing name and namespace with a jsonpath expression.
Answer:
Explanation:
kubectl get pods -o=jsonpath="{.items[*]['metadata.name' , 'metadata.namespace']}"
NEW QUESTION # 35
List all the pods sorted by created timestamp
Answer:
Explanation:
See the solution below.
Explanation
kubect1 get pods--sort-by=.metadata.creationTimestamp
NEW QUESTION # 36
Set CPU and memory requests and limits for existing pod name
"nginx-prod".
Set requests for CPU and Memory as 100m and 256Mi respectively
Set limits for CPU and Memory as 200m and 512Mi respectively
- A. kubectl get po
kubectl set resources po nginx-prod --
limits=cpu=200m,memory=512Mi --requests=cpu=100m,memory=256Mi
//Verify
kubectl describe po nginx-prod - B. kubectl get po
kubectl set resources po nginx-prod --
limits=cpu=200m,memory=512Mi --requests=cpu=100m,memory=256Mi
//Verify
kubectl top po
kubectl describe po nginx-prod
Answer: B
NEW QUESTION # 37
Set the node named ek8s-node-1 as unavailable and reschedule all the pods running on it.
Answer:
Explanation:
solution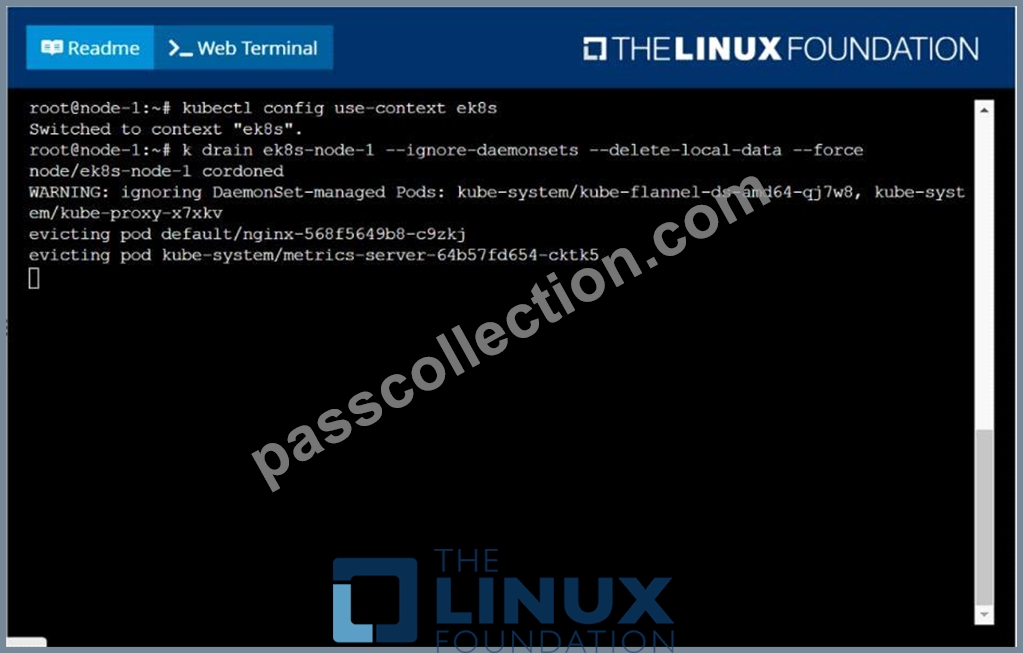
NEW QUESTION # 38
Monitor the logs of pod foo and:
Extract log lines corresponding
unable-to-access-website
Write them to/opt/KULM00201/foo
Answer:
Explanation:
See the solution below.
Explanation
solution
F:\Work\Data Entry Work\Data Entry\20200827\CKA\1 B.JPG
F:\Work\Data Entry Work\Data Entry\20200827\CKA\1 C.JPG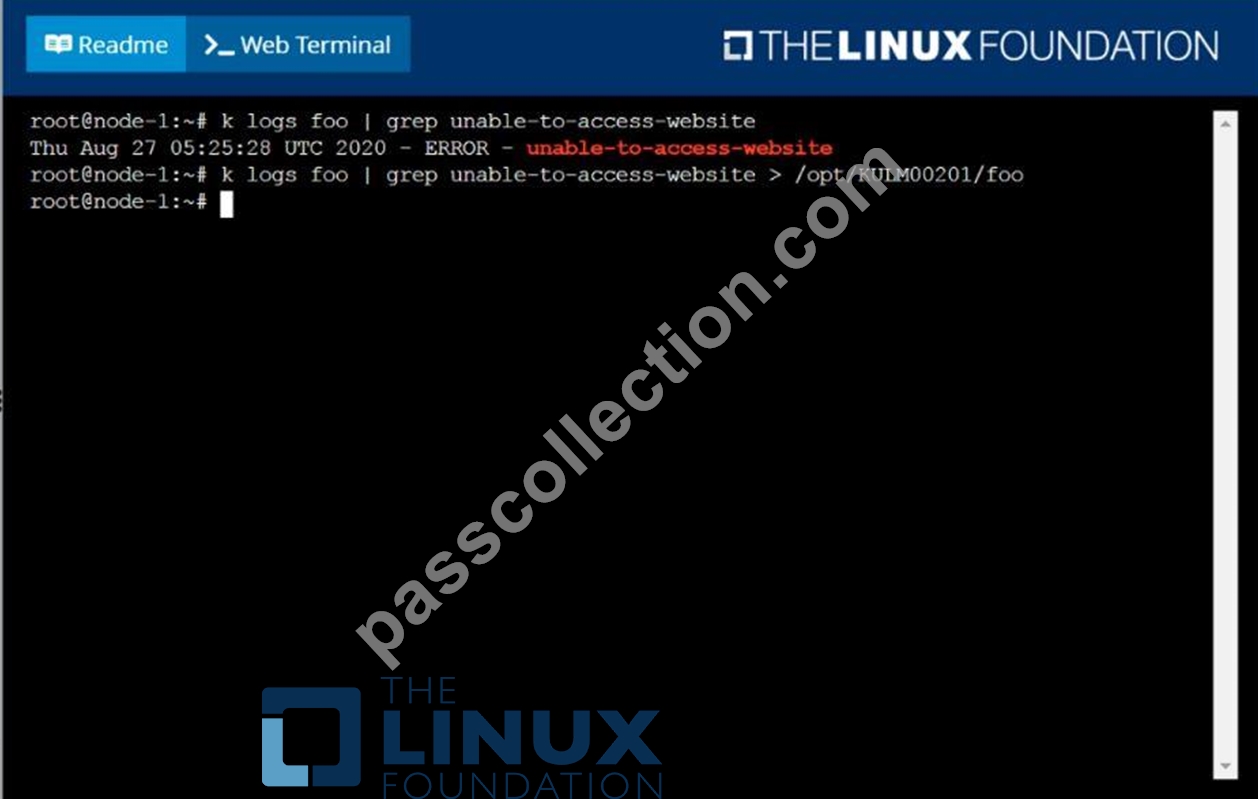
NEW QUESTION # 39
Create a snapshot of theetcdinstance running at , saving thesnapshot to the file path
/srv/data/etcd-snapshot.db.
The following TLScertificates/key are suppliedfor connecting to the server withetcdctl:
* CA certificate:/opt/KUCM00302/ca.crt
* Client certificate:/opt/KUCM00302/etcd-client.crt
* Client key:Topt/KUCM00302/etcd-client.key
Answer:
Explanation:
See the solution below.
Explanation
solution
NEW QUESTION # 40
Scale down the deployment to 1 replica
Answer:
Explanation:
kubectl scale deployment webapp -replicas=1 //Verify kubectl get deploy kubectl get po,rs
NEW QUESTION # 41
Modify "hello-job" and make it run 10 times one after one and 5 times parallelism: 5
- A. kubectl create job hello-job --image=busybox --dry-run -o yaml
-- echo "Hello I am from job" > hello-job.yaml
// edit the yaml file to add completions: 16 and
kubectl create -f hello-job.yaml
YAML File:
apiVersion: batch/v1
kind: Job
metadata:
name: hello-job
spec:
completions: 16
parallelism: 5
template:
metadata:
spec:
containers:
- command:
- echo
- Hello I am from job
image: busybox
name: hello-job
restartPolicy: Never - B. kubectl create job hello-job --image=busybox --dry-run -o yaml
-- echo "Hello I am from job" > hello-job.yaml
// edit the yaml file to add completions: 10 and
kubectl create -f hello-job.yaml
YAML File:
apiVersion: batch/v1
kind: Job
metadata:
name: hello-job
spec:
completions: 10
parallelism: 5
template:
metadata:
spec:
containers:
- command:
- echo
- Hello I am from job
image: busybox
name: hello-job
restartPolicy: Never
Answer: B
NEW QUESTION # 42
Get list of PVs and order by size and write to file - /opt/pvlist.txt
Answer:
Explanation:
kubectl get pv --sort-by=.spec.capacity.storage > /opt/pvlist.txt
NEW QUESTION # 43
Configure the kubelet systemd- managed service, on the node labelled with name=wk8s-node-1, to launch a pod containing a single container of Image httpd named webtool automatically. Any spec files required should be placed in the /etc/kubernetes/manifests directory on the node.
You can ssh to the appropriate node using:
[student@node-1] $ ssh wk8s-node-1
You can assume elevated privileges on the node with the following command:
[student@wk8s-node-1] $ | sudo -i
Answer:
Explanation:
See the solution below.
Explanation
solution
F:\Work\Data Entry Work\Data Entry\20200827\CKA\21 C.JPG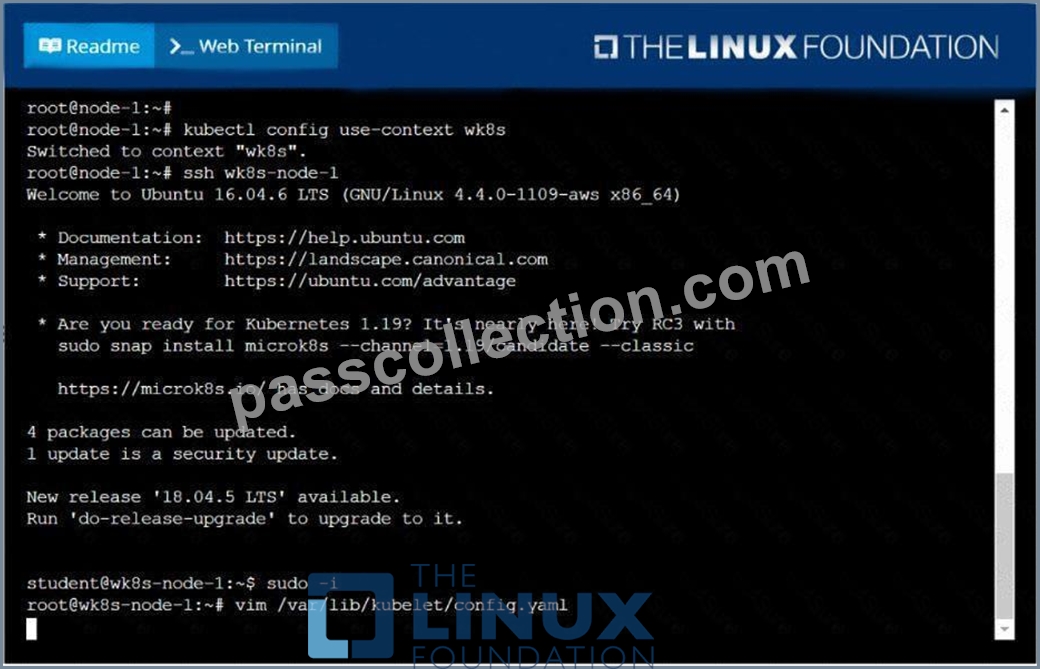
F:\Work\Data Entry Work\Data Entry\20200827\CKA\21 D.JPG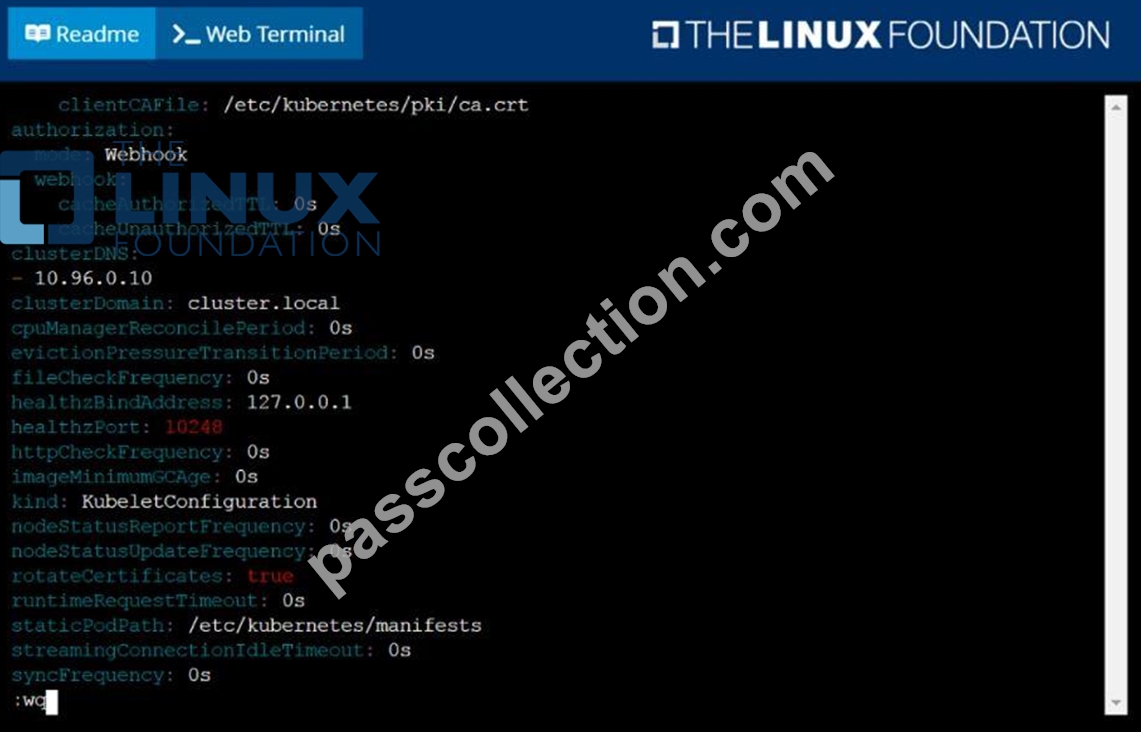
F:\Work\Data Entry Work\Data Entry\20200827\CKA\21 E.JPG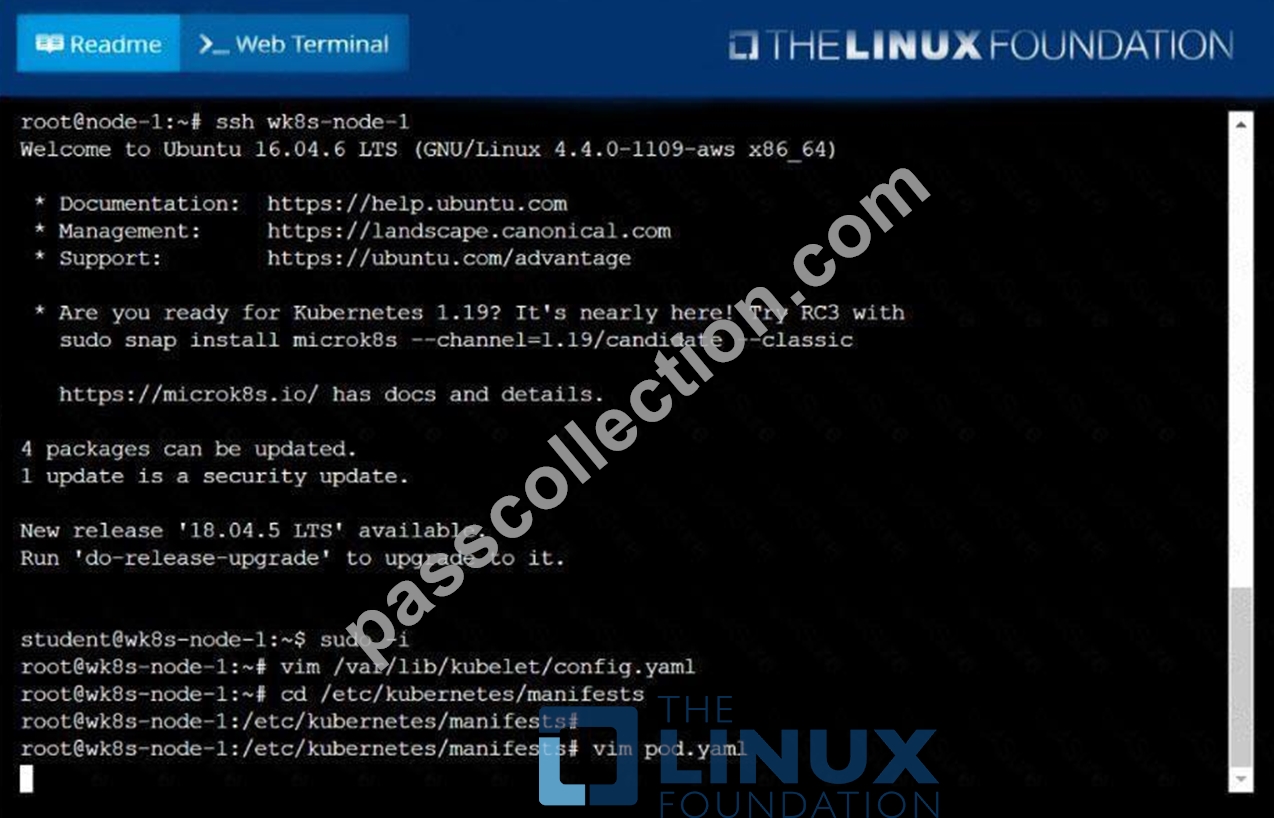
F:\Work\Data Entry Work\Data Entry\20200827\CKA\21 F.JPG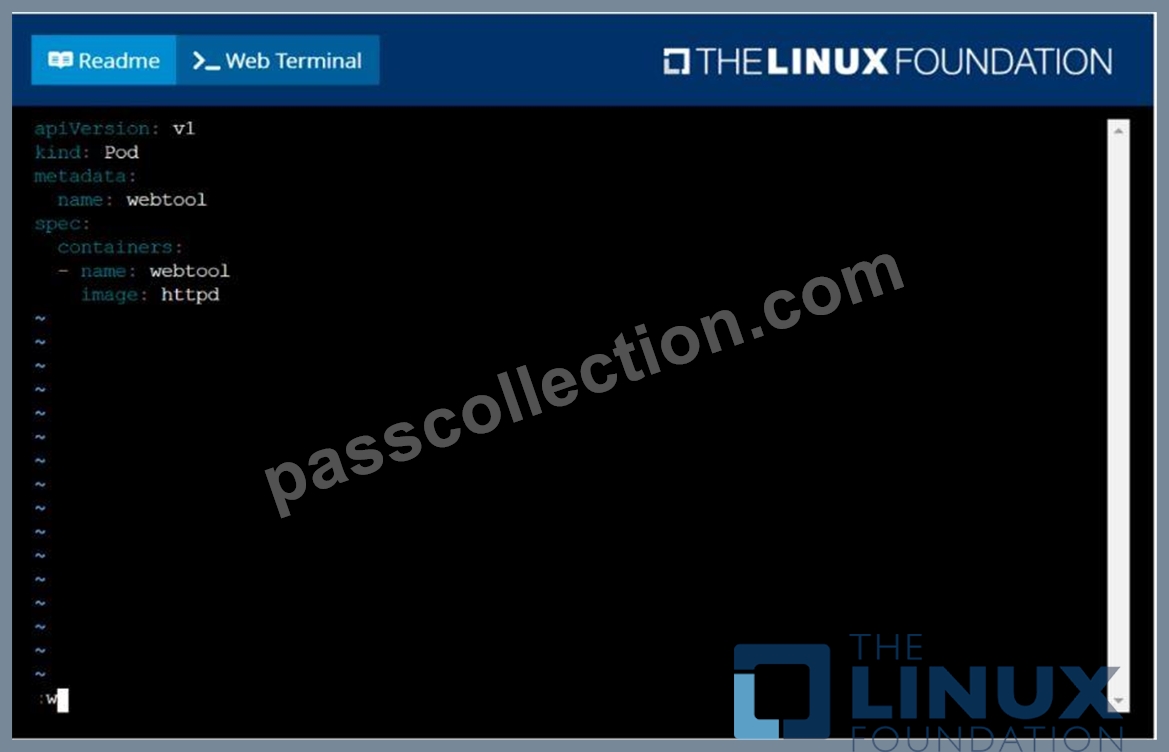
F:\Work\Data Entry Work\Data Entry\20200827\CKA\21 G.JPG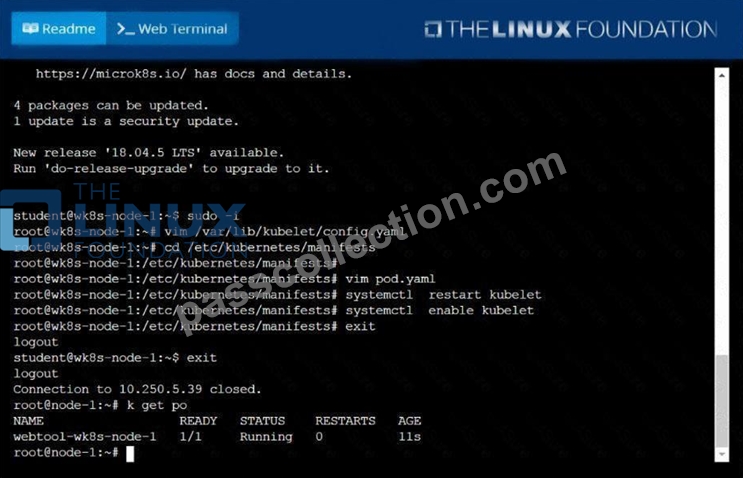
NEW QUESTION # 44
Create a deployment as follows:
* Name: nginx-random
* Exposed via a service nginx-random
* Ensure that the service & pod are accessible via their respective DNS records
* The container(s) within any pod(s) running as a part of this deployment should use the nginx Image Next, use the utility nslookup to look up the DNS records of the service & pod and write the output to
/opt/KUNW00601/service.dns and /opt/KUNW00601/pod.dns respectively.
Answer:
Explanation:
See the solution below.
Explanation
Solution: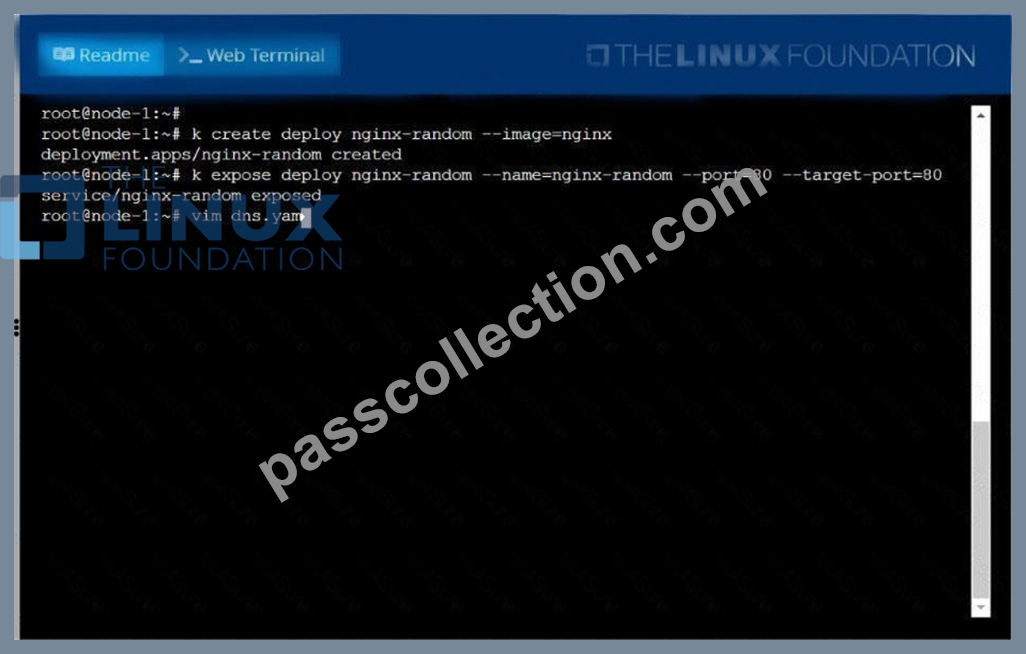
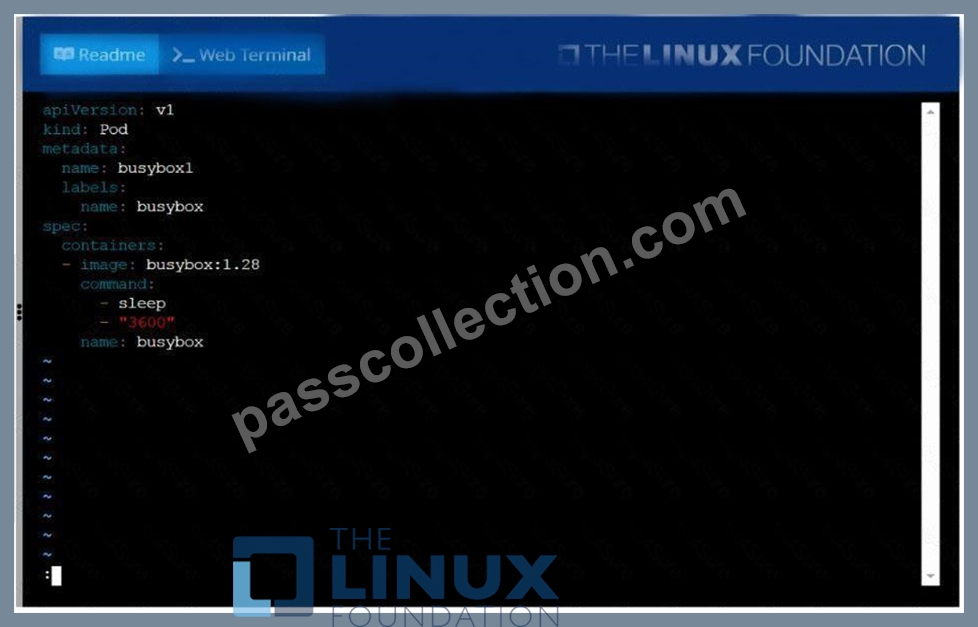

NEW QUESTION # 45
Score: 4%
Task
Check to see how many nodes are ready (not including nodes tainted NoSchedule ) and write the number to
/opt/KUSC00402/kusc00402.txt
Answer:
Explanation:
See the solution below.
Explanation
Solution:
kubectl describe nodes | grep ready|wc -l
kubectl describe nodes | grep -i taint | grep -i noschedule |wc -l
echo 3 > /opt/KUSC00402/kusc00402.txt
#
kubectl get node | grep -i ready |wc -l
# taintsnoSchedule
kubectl describe nodes | grep -i taints | grep -i noschedule |wc -l
#
echo 2 > /opt/KUSC00402/kusc00402.txt
NEW QUESTION # 46
......
The CKA Program Certification Exam covers a wide range of topics related to Kubernetes. These topics include installation and configuration, networking, scheduling, security, storage, and troubleshooting. Candidates must have a deep understanding of these topics in order to pass the exam. They must also be able to perform common Kubernetes tasks quickly and accurately.
CKA Dumps for Kubernetes Administrator Certified Exam Questions and Answer: https://www.passcollection.com/CKA_real-exams.html
Realistic Verified CKA exam dumps Q&As - CKA Free Update: https://drive.google.com/open?id=11vWHfpLIBDDuukQ8YRwf3OMpe6QTj1YN
