

[Jan 25, 2022] Pass NSE5_FMG-6.2 Review Guide, Reliable NSE5_FMG-6.2 Test Engine
NSE5_FMG-6.2 Test Engine Practice Test Questions, Exam Dumps
NEW QUESTION 33
Which two statements regarding device management on FortiManager are true? (Choose two.)
- A. FortiGate in transparent mode configurations are not counted toward the device count on FortiManager.
- B. The maximum number of managed devices for each ADOM is 500.
- C. FortiGate devices in an HA cluster that has five VDOMs are counted as five separate devices.
- D. FortiGate devices in HA cluster devices are counted as a single device.
Answer: C,D
NEW QUESTION 34
View the following exhibit.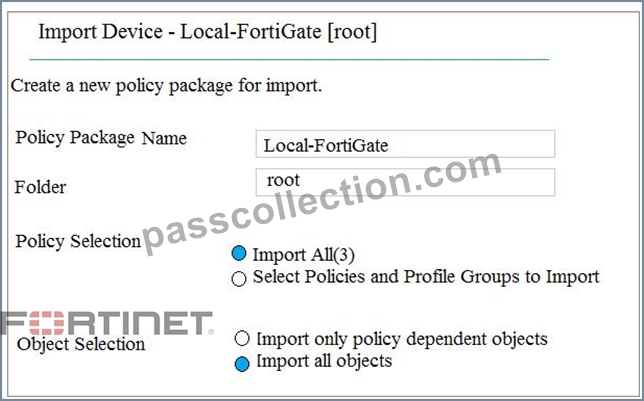
An administrator is importing a new device to FortiManager and has selected the shown options. What will happen if the administrator makes the changes and installs the modified policy package on this managed FortiGate?
- A. The unused objects that are not tied to the firewall policies will remain as read-only locally on FortiGate
- B. The unused objects that are not tied to the firewall policies locally on FortiGate will be deleted
- C. The unused objects that are not tied to the firewall policies in policy package will be deleted from the FortiManager database
- D. The unused objects that are not tied to the firewall policies will be installed on FortiGate
Answer: B
NEW QUESTION 35
Refer to the exhibit. Given the configurations shown in the exhibit, what can you conclude from the installation targets in the Install On column?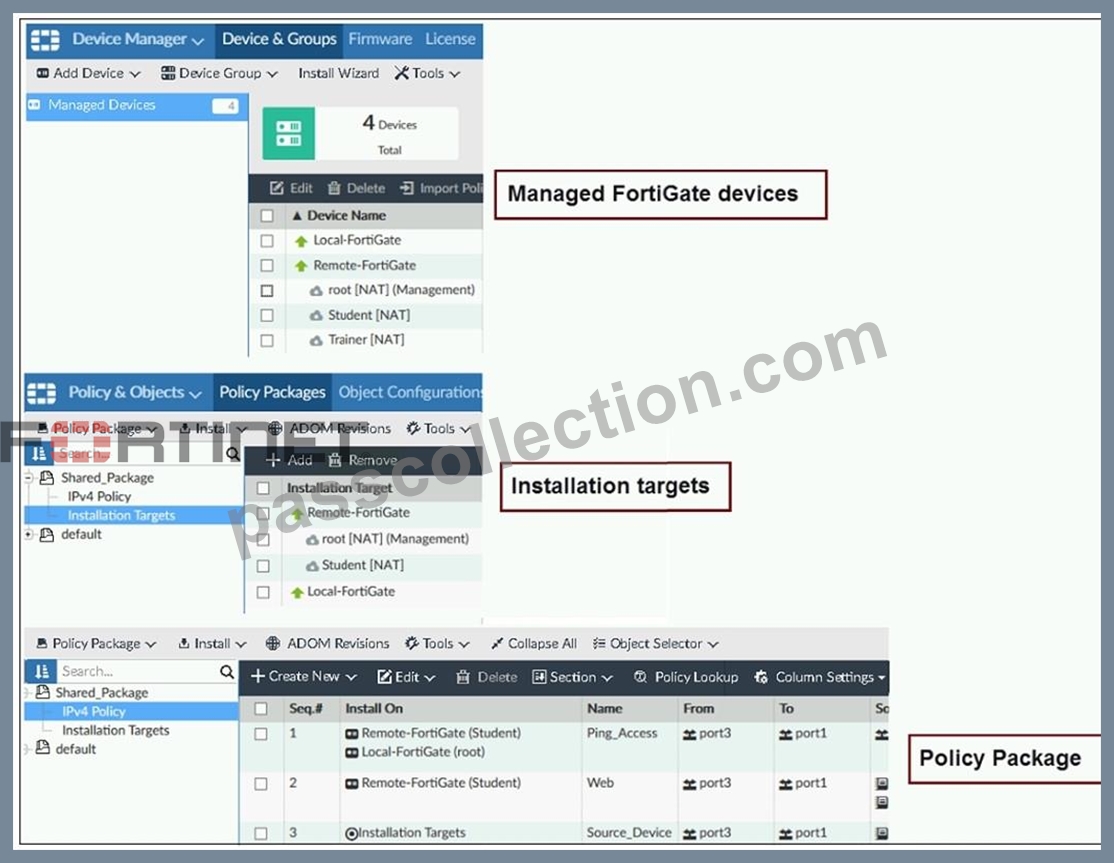
- A. The Install On column value represents successful installations on the managed devices.
- B. Policy seq.# 3 will be installed on all managed devices and VDOMs that are listed under Installation Targets.
- C. Policy seq.# 3 will be installed on the Trainer[NAT] VDOM only.
- D. Policy seq.# 3 will not be installed on any managed device.
Answer: B
NEW QUESTION 36
Refer to the following exhibit: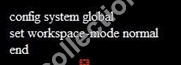
Which of the following statements are true based on this configuration? (Choose two.)
- A. Ungraceful closed sessions will keep the ADOM in a locked state until the administrator session times out
- B. Unlocking an ADOM will install configuration automatically on managed devices
- C. Unlocking an ADOM will submit configuration changes automatically to the approval administrator
- D. The same administrator can lock more than one ADOM at the same time
Answer: A,D
Explanation:
To enable ADOM locking and disable concurrent ADOM access:
config system global
set workspace-mode normal
end
Reference: http://help.fortinet.com/fmgr/cli/5-6-2/Document/0800_ADOMs/200_Configuring+.htm
NEW QUESTION 37
Which two statements about Security Fabric integration with FortiManager are true? (Choose two.)
- A. The Security Fabric settings are part of the device level settings
- B. The Fabric View module enables you to view the Security Fabric ratings for Security Fabric devices
- C. The Fabric View module enables you to generate the Security Fabric ratings for Security Fabric devices
- D. The Security Fabric license, group name and password are required for the FortiManager Security Fabric integration
Answer: A,B
NEW QUESTION 38
View the following exhibit. An administrator is importing a new device to FortiManager and has selected the shown options.
What will happen if the administrator makes the changes and installs the modified policy package on this managed FortiGate?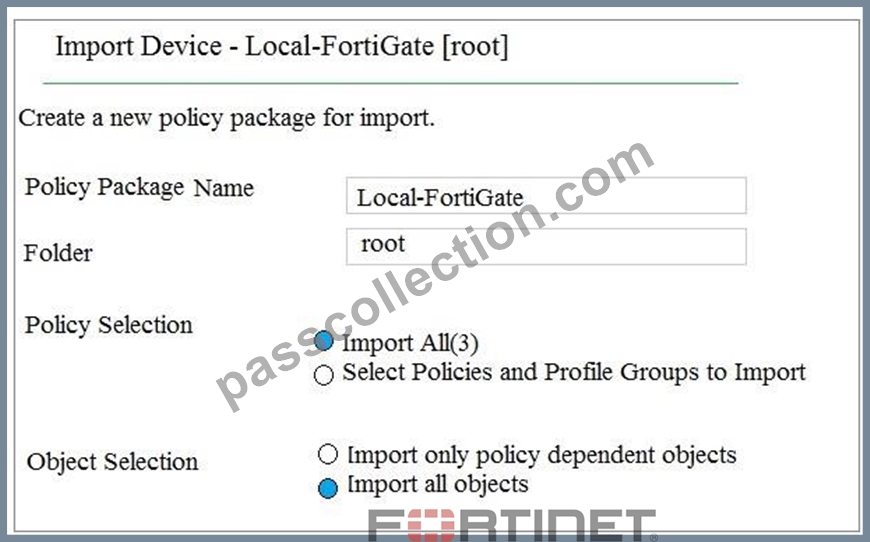
- A. The unused objects that are not tied to the firewall policies will remain as read-only locally on FortiGate
- B. The unused objects that are not tied to the firewall policies locally on FortiGate will be deleted
- C. The unused objects that are not tied to the firewall policies in policy package will be deleted from the FortiManager database
- D. The unused objects that are not tied to the firewall policies will be installed on FortiGate
Answer: B
Explanation:
Regardless of whether you choose to import only policy-dependent objects or all objects, the system will delete orphan (unused) object that are not tied to policies locally on FortiGate in the next installation.
NEW QUESTION 39
In addition to the default ADOMs, an administrator has created a new ADOM named Training for FortiGate devices.
The administrator sent a device registration to FortiManager from a remote FortiGate. Which one of the following statements is true?
- A. The FortiGate will be automatically added to the Training ADOM.
- B. By default, the unregistered FortiGate will appear in the root ADOM.
- C. The FortiGate will be added automatically to the default ADOM named FortiGate.
- D. The FortiManager administrator must add the unregistered device manually to the unregistered device manually to the Training ADOM using the Add Device wizard
Answer: B
NEW QUESTION 40
What configuration setting for FortiGate is part of a device-level database on FortiManager?
- A. Firewall policies
- B. VIP and IP Pools
- C. Routing
- D. Security profiles
Answer: C
Explanation:
The device-level database includes configuration details related to device-level settings, such as interfaces, DNS, routing, and more.
The ADOM-level database includes configuration details related to firewall policies, objects, and security profiles.
NEW QUESTION 41
View the following exhibit.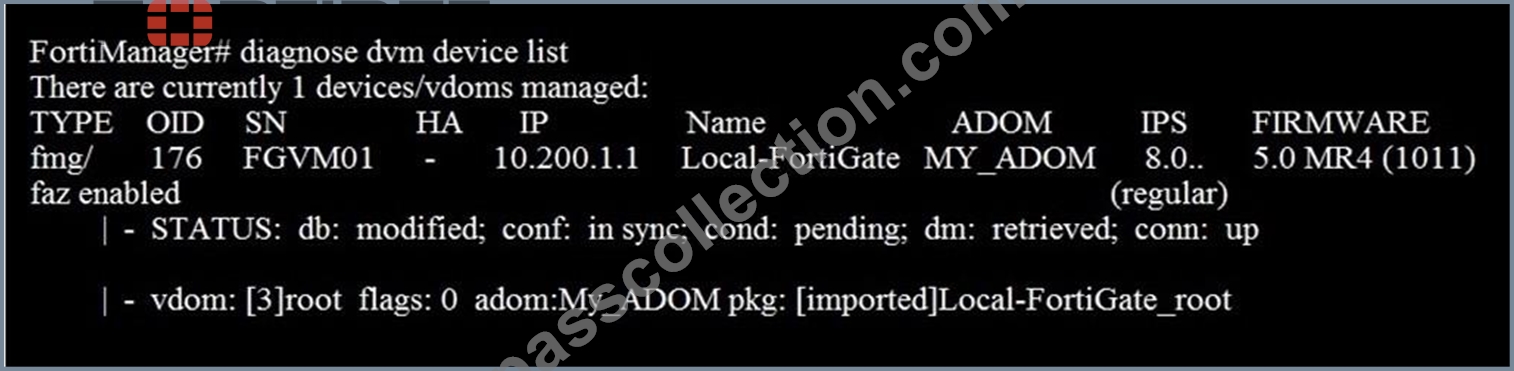
What of the following statements are true regarding the output? (Choose two.)
- A. The latest revision history for the managed FortiGate does match with the FortiGate running configuration
- B. Configuration changes directly made on the FortiGate have been automatically updated to device-level database
- C. The latest history for the managed FortiGate does not match with the device-level database
- D. Configuration changes have been installed to FortiGate and represents FortiGate configuration has been changed
Answer: A,B
Explanation:
This example shows that FortiGate configuration is in sync with the latest running revision history. However, change have been made to device-level settings.
Once the changes are installed on FortiGate, it will show db: unmodified and cond:OK.
NEW QUESTION 42
View the following exhibit.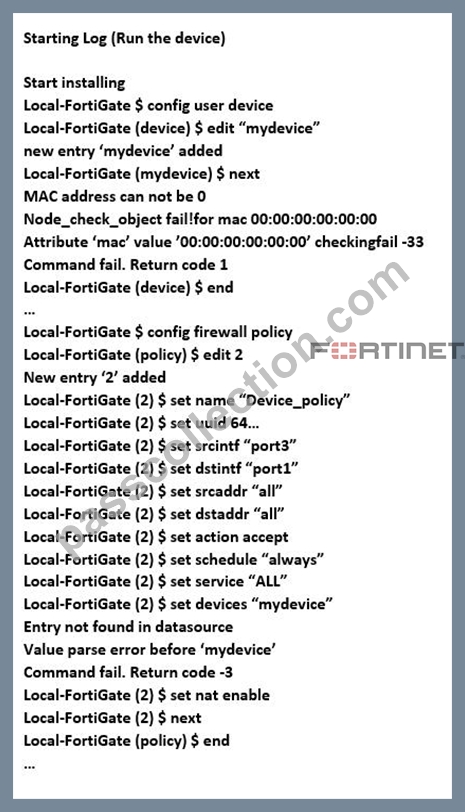
Which statement is true regarding this failed installation log?
- A. Policy ID 2 will not be installed
- B. Policy ID 2 is installed without a source device
- C. Policy ID 2 is installed without a source address
- D. Policy ID 2 is installed in disabled state
Answer: B
NEW QUESTION 43
View the following exhibit.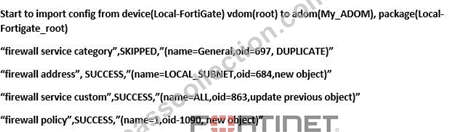
Which one of the following statements is true regarding the object named ALL?
- A. FortiManager updated the object ALL using FortiManager's value in its database
- B. FortiManager created the object ALL as a unique entity in its database, which can be only used by this managed FortiGate.
- C. FortiManager installed the object ALL with the updated value.
- D. FortiManager updated the object ALL using FortiGate's value in its database
Answer: D
Explanation:
If a conflict is detected, FortiManager updates the object associated with the selected device. When you choose the FortiGate device value and import the address object ALL, an entry named update previous object is added to the import report.
NEW QUESTION 44
An administrator with the Super_Userprofile is unable to log in to FortiManager because of an authentication failure message.
Which troubleshooting step should you take to resolve the issue?
- A. Make sure ADOMs are enabled and the administrator has access to the Global ADOM
- B. Make sure FortiManager Access is enabled in the administrator profile
- C. Make sure the administrator IP address is part of the trusted hosts
- D. Make sure Offline Mode is disabled
Answer: C
Explanation:
Explanation
NEW QUESTION 45
View the following exhibit.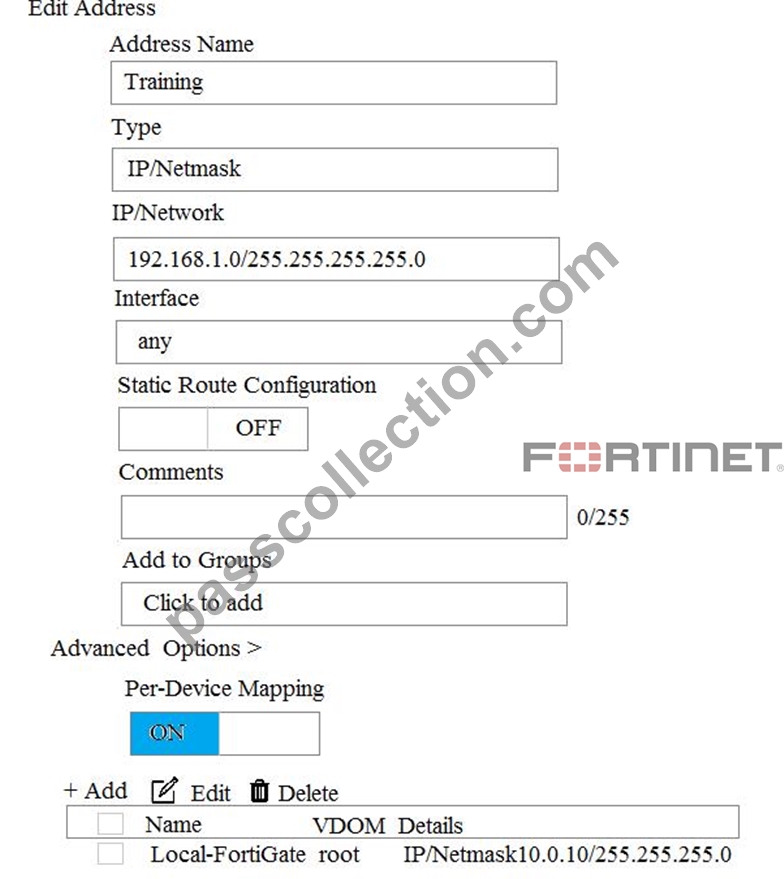
An administrator has created a firewall address object, Training, which is used in the Local-FortiGate policy package. When the install operation is performed, which IP Netmask will be installed on the Local-FortiGate, for the Training firewall address object?
- A. 10.0.1.0/24
- B. 192.168.0.1/24
- C. Local-FortiGate will automatically choose an IP Network based on its network interface settings.
- D. It will create firewall address group on Local-FortiGate with 192.168.0.1/24 and 10.0.1.0/24 object values
Answer: A
NEW QUESTION 46
What is the purpose of ADOM revisions?
- A. To save the current state of all policy packages and objects for an ADOM.
- B. To revert individual policy packages and device-level settings for a managed FortiGate by reverting to a specific ADOM revision
- C. To create System Checkpoints for the FortiManager configuration.
- D. To save the current state of the whole ADOM.
Answer: A
NEW QUESTION 47
View the following exhibit: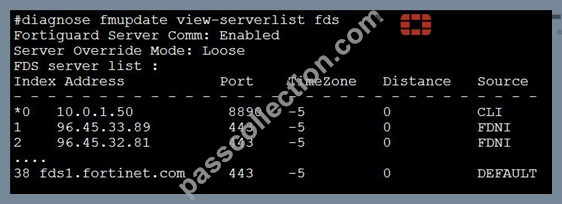
How will FortiManager try to get updates for antivirus and IPS?
- A. From public FDNI server with highest index number only
- B. From the default server fdsl.fortinet.com
- C. From the list of configured override servers with ability to fall back to public FDN servers
- D. From the configured override server list only
Answer: C
NEW QUESTION 48
View the following exhibit: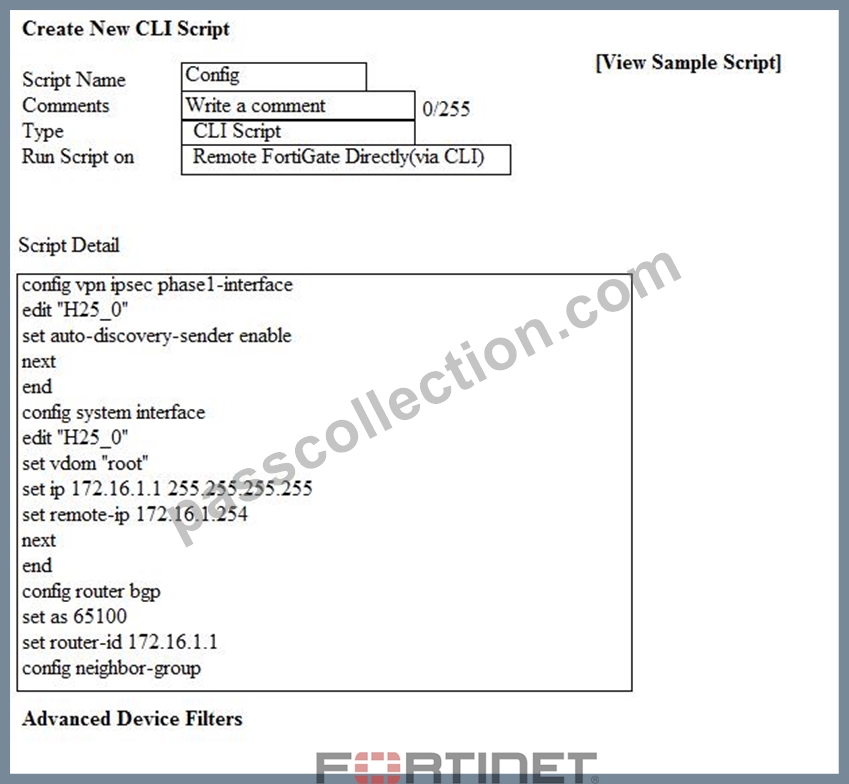
Which of the following statements are true if the scripts is executed using Remote FortiGate Directly (via CLI) option? (Choose two.)
- A. You must install these changes using Install Wizard
- B. FortiManager will create a new revision history.
- C. FortiGate will auto-update the FortiManager's device-level database.
- D. FortiManager provides a preview of CLI commands before executing this script on a managed FortiGate.
Answer: B,C
NEW QUESTION 49
What does the diagnose dvm check-integrity command do? (Choose two.)
- A. Verifies and corrects unregistered, registered, and deleted device states
- B. Verifies and corrects duplicate VDOM entries
- C. Verifies and corrects database schemas in all object tables
- D. Internally upgrades existing ADOMs to the same ADON version in order to clean up and correct the ADOM syntax
Answer: A,B
Explanation:
6.2 Study Guide page 305
verify and correct parts of the device manager databases, including:
- inconsistent device-to-group and group-to-ADOM memberships
- unregistered, registered, and deleted device states
- device lock statuses
- duplicate VDOM entries
NEW QUESTION 50
Which of the following conditions trigger FortiManager to create a new revision history? (Choose two.)
- A. When FortiManager is auto-updated with configuration changes made directly on a managed device
- B. When changes to device-level database is made on FortiManager
- C. When configuration revision is reverted to previous revision in the revision history
- D. When FortiManager installs device-level changes to a managed device
Answer: A,D
Explanation:
When a new configuration is installed, FortiManager compares the latest revision history running on the device with the changes made on FortiManager.
FortiManager then creates a new revision in the revision history and installs these changes on the managed device. Modifying configuration directly on a managed device creates automatically new revision.
NEW QUESTION 51
Refer to the exhibit.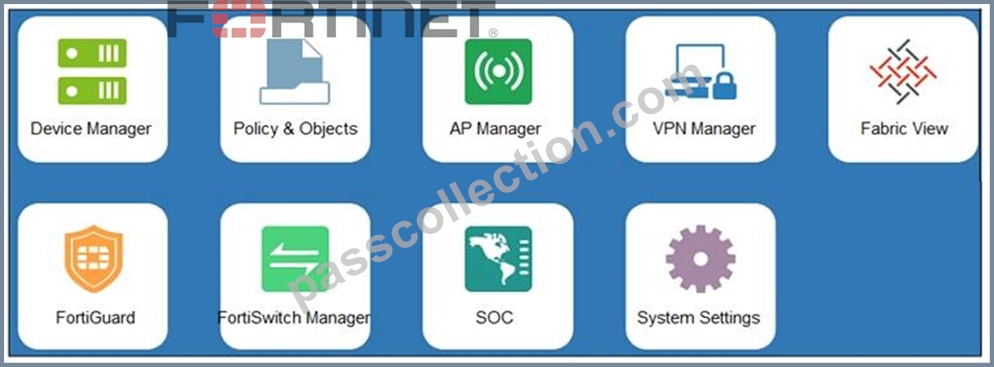
An administrator logs into the FortiManager GUI and sees the panes shown in the exhibit.
Which two reasons can explain why the FortiAnalyzer feature panes do not appear? (Choose two.)
- A. The administrator IP address is not a part of the trusted hosts configured on FortiManager interfaces.
- B. The administrator profile does not have full access privileges like the Super_User profile.
- C. The administrator logged in using the unsecure protocol HTTP, so the view is restricted.
- D. FortiAnalyzer features are not enabled on FortiManager.
Answer: A,D
NEW QUESTION 52
View the following exhibit.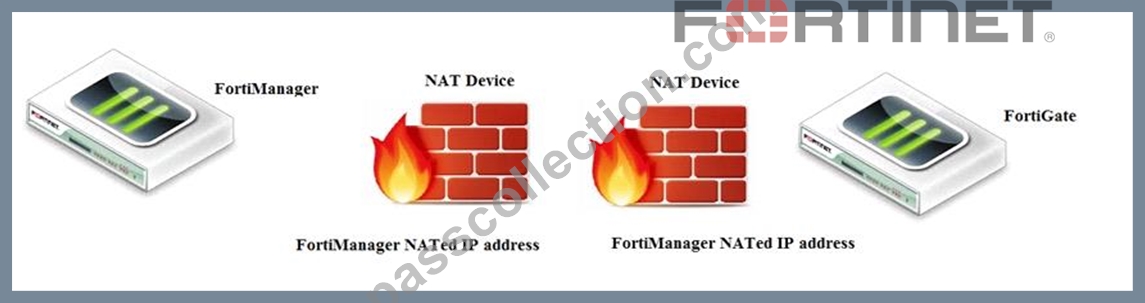
Which of the following statements are true if FortiManager and FortiGate are behind the NAT devices? (Choose two.)
- A. During discovery, the FortiManager NATed IP address is not set by default on FortiGate.
- B. If the FCFM tunnel is torn down, FortiManager will try to re-establish the FGFM tunnel.
- C. FortiGate is discovered by FortiManager through the FortiGate NATed IP address.
- D. FortiGate can announce itself to FortiManager only if the FortiManager IP address is configured on FortiGate under central management.
Answer: C,D
NEW QUESTION 53
......
100% Free NSE5_FMG-6.2 Daily Practice Exam With 85 Questions: https://www.passcollection.com/NSE5_FMG-6.2_real-exams.html
