

[Jan 19, 2022] Verified AZ-104 dumps and 465 unique questions
AZ-104 Dumps for Pass Guaranteed - Pass AZ-104 Exam 2022
Microsoft AZ-104 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
| Topic 12 |
|
| Topic 13 |
|
| Topic 15 |
|
| Topic 16 |
|
| Topic 17 |
|
| Topic 18 |
|
| Topic 19 |
|
| Topic 20 |
|
| Topic 21 |
|
Why Take This Exam?
The Microsoft AZ-104 is one of the role-based options that were introduced in 2019. Passing it will help a candidate to earn the Microsoft Certified: Azure Administrator Associate certification which is aimed at those specialists who have the relevant skills in implementing and managing a Microsoft Azure environment of an organization. These individuals are the Azure administrators who are responsible for the implementation, management, and monitoring of identity, storage, governance, virtual network, and compute in a Cloud-based environment. They are also in charge of monitoring and adjusting resources when needed. Moreover, these employees function as a part of a bigger team that is focused on implementing the Cloud infrastructure of their company. So, if you want to become such a highly competent specialist, you need to know certain things before going for the Microsoft AZ-104 test.
NEW QUESTION 178
You need to define a custom domain name for Azure AD to support the planned infrastructure.
Which domain name should you use?
- A. Install Azure AD Connect on a server in the Miami office and enable Pass-through Authentication
- B. Install the Active Directory Federation Services (AD FS) role on a domain controller in the Miami office.
- C. Join the client computers in the Miami office to Azure AD.
- D. Allow inbound TCP port 8080 to the domain controllers in the Miami office.
- E. Add http://autologon.microsoftazuread-sso.com to the intranet zone of each client computer in the Miami office.
Answer: A,E
Explanation:
Every Azure AD directory comes with an initial domain name in the form of domainname.onmicrosoft.com. The initial domain name cannot be changed or deleted, but you can add your corporate domain name to Azure AD as well. For example, your organization probably has other domain names used to do business and users who sign in using your corporate domain name. Adding custom domain names to Azure AD allows you to assign user names in the directory that are familiar to your users, such as '[email protected].' instead of 'alice@domain name.onmicrosoft.com'.
Scenario:
Network Infrastructure: Each office has a local data center that contains all the servers for that office. Each office has a dedicated connection to the Internet.
Humongous Insurance has a single-domain Active Directory forest named humongousinsurance.com Planned Azure AD Infrastructure: The on-premises Active Directory domain will be synchronized to Azure AD.
References: https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/add-custom-domain
NEW QUESTION 179
Hotspot Question
You have an Azure Active Directory (Azure AD) tenant named adatum.com. Adatum.com contains the groups in the following table.
You create two user accounts that are configured as shown in the following table.
To which groups do User1 and User2 belong? To answer. select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
https://docs.microsoft.com/en-us/sccm/core/clients/manage/collections/create-collections
NEW QUESTION 180
You have an Azure subscription that contains an Azure Service Bus named Bus1.
Your company plans to deploy two Azure web apps named App1 and App2. The web apps will create messages that have the following requirements:
* Each message created by App1 must be consumed by only a single consumer
* Each message created by App2 will be consumed by multiple consumers.
Which resource should you create for each web app? To answer, drag the appropriate resources to the correct web apps. Each resource may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/azure/service-bus-messaging/service-bus-queues-topics-subscriptions
NEW QUESTION 181
You have an Azure virtual machine mat runs Windows Server 2019 and has the following configurations:
* Name:VM1
* Location: Welt US
* Connected to: VNfT1
* Private IP address: 10.1.0.4
* Public IP address: 52 18685.63
* DNS suffix m Windows Server.Adatum.com
You create the Azure DNS zones shown in the following table.

Answer:
Explanation:
NEW QUESTION 182
You have an Azure subscription that contains the resources shown in the following table.
The Not allowed resource types Azure policy is assigned to RG1 and uses the following parameters:
* Microsoft.Network/virtualNetwork
* Microsoft.Compute/virtualMachines
In RG1, you need to create a new virtual machine named VM2, and then connect VM2 to VNET1.
What should you do first?
- A. Create an Azure Resource Manager template
- B. Remove Microsoft.Compute/virtualMachines from the policy
- C. Add a subnet to VNET1
- D. Remove Microsoft.Network/virtualNetworks from the policy
Answer: B
Explanation:
Explanation
The Not allowed resource types Azure policy prohibits the deployment of specified resource types. You specify an array of the resource types to block.
Virtual Networks and Virtual Machines are prohibited.
Reference:
https://docs.microsoft.com/en-us/azure/governance/policy/samples/
NEW QUESTION 183
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure virtual machine named VM1. VM1 was deployed by using a custom Azure Resource Manager template named ARM1.json.
You receive a notification that VM1 will be affected by maintenance.
You need to move VM1 to a different host immediately.
Solution: From the Update management blade, you click enable.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
You would need to Redeploy the VM.
References:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/redeploy-to-new-node
NEW QUESTION 184
You have an Azure subscription named Subscription1. Subscription1 contains the resources in the following table.
VNet1 is in RG1. VNet2 is in RG2. There is no connectivity between VNet1 and Vnet2.
An administrator named Admin1 creates an Azure virtual machine named VM1 in RG1. VM1 uses a disk named Disk1 and connects to VNet1. Admin1 then installs a custom application in VM1.
You need to move the custom application to Vnet2. The solution must minimize administrative effort.
Which two actions should you perform? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
We cannot just move a virtual machine between networks. What we need to do is identify the disk used by the VM, delete the VM itself while retaining the disk, and recreate the VM in the target virtual network and then attach the original disk to it.
First action: Delete VM1
Second action: Create a new virtual machine
Reference:
https://docs.microsoft.com/en-us/archive/blogs/canitpro/step-by-step-move-a-vm-to-a-different-vnet-on-azure
https://4sysops.com/archives/move-an-azure-vm-to-another-virtual-network-vnet/#migrate-an-azure-vmbetween-vnets
NEW QUESTION 185
You have an Azure subscription that contains the virtual networks shown in the following table.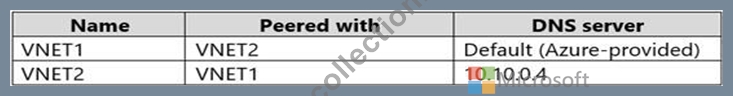
You have the virtual machines shown in the following table.
You have the virtual network interfaces shown in the following table.
Server1 is a DNS server that contains the resources shown in the following table.
You have an Azure private DNS zone named contoso.com that has a virtual network link to VNET2 and the records shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
A picture containing text, indoor, screenshot Description automatically generated
NEW QUESTION 186
You need to configure the Device settings to meet the technical requirements and the user requirements.
Which two settings should you modify? To answer, select the appropriate settings in the answer area.
Answer:
Explanation:
Explanation

Box 1: Selected
Only selected users should be able to join devices
Box 2: Yes
Require Multi-Factor Auth to join devices.
From scenario:
* Ensure that only users who are part of a group named Pilot can join devices to Azure AD
* Ensure that when users join devices to Azure Active Directory (Azure AD), the users use a mobile phone to verify their identity.
NEW QUESTION 187
You have an Azure subscription named Subscription' that contains an Azure Log Analytics workspace named Workspace', You need to view the error events from a table named Event.
Which query should you run in Workspace1?
- A. select * from Event where EventType is "error"
- B. search in (Event) "error"
- C. Event | where EventType is "error"
- D. search in (Event) * | where EventType -eq "error"
Answer: B
NEW QUESTION 188
You have an Azure subscription that contains the resources in the following table.
VM1 and VM2 are deployed from the same template and host line-of-business applications accessed by using Remote Desktop. You configure the network security group (NSG) shown in the exhibit. (Click the Exhibit button.)
You need to prevent users of VM1 and VM2 from accessing websites on the Internet.
What should you do?
- A. Associate the NSG to Subnet1.
- B. Change the Port_80 inbound security rule.
- C. Disassociate the NSG from a network interface.
- D. Change the DenyWebSites outbound security rule.
Answer: A
Explanation:
Explanation
You can associate or dissociate a network security group from a network interface or subnet.
The NSG has the appropriate rule to block users from accessing the Internet. We just need to associate it with Subnet1.
References: https://docs.microsoft.com/en-us/azure/virtual-network/manage-network-security-group
NEW QUESTION 189
You have an Azure subscription that contains an Azure Service Bus named Bus1.
Your company plans to deploy two Azure web apps named App1 and App2. The web apps will create messages that have the following requirements:
* Each message created by App1 must be consumed by only a single consumer
* Each message created by App2 will be consumed by multiple consumers.
Which resource should you create for each web app? To answer, drag the appropriate resources to the correct web apps. Each resource may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/service-bus-messaging/service-bus-queues-topics-subscriptions
NEW QUESTION 190
You have an Azure subscription named Subscription1.
You plan to deploy an Ubuntu Server virtual machine named VM1 to Subscription1.
You need to perform a custom deployment of the virtual machine. A specific trusted root certification authority (CA) must be added during the deployment.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure/virtual-machines/linux/tutorial-automate-vm-deployment
NEW QUESTION 191
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table:
User3 is the owner of Group1.
Group2 is a member of Group1.
You configure an access review named Review1 as shown in the following exhibit:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
In the Users section, specify the users that the access review applies to. Access reviews can be for the members of a group or for users who were assigned to an application. You can further scope the access review to review only the guest users who are members (or assigned to the application), rather than reviewing all the users who are members or who have access to the application.
Present Use Case:
Group2 is a member of Group1 and User3 is the owner of Group1 So User3 can review both Group 1 and 2.
But for review the scope says only Guest.
Solution:
User1 is a member not a guest so 1st statement ==> NO
UserA is member not the guest so 2nd statement ==> No
UserB is a guest so 3rd statement ==> Yes
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/create-access-review
NEW QUESTION 192
You have an Azure virtual machine named VM1 and a Recovery Services vault named Vault1.
You create a backup Policy1 as shown in the exhibit. (Click the Exhibit tab.)
You configure the backup of VM1 to use Policy1 on Thursday, January 1.
You need to identify the number of available recovery points for VM1.
How many recovery points are available on January 8 and on January 15? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: 6
4 daily + 1 weekly + monthly
Box 2: 8
4 daily + 2 weekly + monthly + yearly
NEW QUESTION 193
You need to meet the connection requirements for the New York office.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 1: Create a virtual network gateway and a local network gateway.
Azure VPN gateway. The VPN gateway service enables you to connect the VNet to the on-premises network through a VPN appliance. For more information, see Connect an on-premises network to a Microsoft Azure virtual network. The VPN gateway includes the following elements:
* Virtual network gateway. A resource that provides a virtual VPN appliance for the VNet. It is responsible for routing traffic from the on-premises network to the VNet.
* Local network gateway. An abstraction of the on-premises VPN appliance. Network traffic from the cloud application to the on-premises network is routed through this gateway.
* Connection. The connection has properties that specify the connection type (IPSec) and the key shared with the on-premises VPN appliance to encrypt traffic.
* Gateway subnet. The virtual network gateway is held in its own subnet, which is subject to various requirements, described in the Recommendations section below.
Box 2: Configure a site-to-site VPN connection
On premises create a site-to-site connection for the virtual network gateway and the local network gateway.
Scenario: Connect the New York office to VNet1 over the Internet by using an encrypted connection.
NEW QUESTION 194
You need to define a custom domain name for Azure AD to support the planned infrastructure.
Which domain name should you use?
- A. humongousinsurance.local
- B. humongousinsurance.onmicrosoft.com
- C. ad.humongousinsurance.com
- D. humongousinsurance.com
Answer: A
Explanation:
Every Azure AD directory comes with an initial domain name in the form of domainname.onmicrosoft.com. The initial domain name cannot be changed or deleted, but you can add your corporate domain name to Azure AD as well. For example, your organization probably has other domain names used to do business and users who sign in using your corporate domain name. Adding custom domain names to Azure AD allows you to assign user names in the directory that are familiar to your users, such as '[email protected].' instead of 'alice@domain name.onmicrosoft.com'.
Scenario:
Network Infrastructure: Each office has a local data center that contains all the servers for that office. Each office has a dedicated connection to the Internet.
Humongous Insurance has a single-domain Active Directory forest named humongousinsurance.com
Planned Azure AD Infrastructure: The on-premises Active Directory domain will be synchronized to Azure AD.
References:
https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/add-custom-domain
NEW QUESTION 195
......
Latest 100% Passing Guarantee - Brilliant AZ-104 Exam Questions PDF: https://www.passcollection.com/AZ-104_real-exams.html
AZ-104 Exam Dumps - Try Best AZ-104 Exam Questions: https://drive.google.com/open?id=1AnLILWYuz9qErWLdqC2h-_nJ14nKIwyf
