

[2021] 300-410 PDF Questions - Perfect Prospect To Go With PassCollection Practice Exam
Cisco 300-410 Pdf Questions - Outstanding Practice To your Exam
NEW QUESTION 124
Which statement about IPv6 ND inspection is true?
- A. It learns and secures bindings for stateless autoconfiguration addresses in Layer 2 neighbor tables.
- B. It learns and secures bindings for stateful autoconfiguration addresses in Layer 3 neighbor tables.
- C. It learns and secures bindings for stateless autoconfiguration addresses in Layer 3 neighbor tables.
- D. It learns and secures bindings for stateful autoconfiguration addresses in Layer 2 neighbor tables.
Answer: A
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/15-s/ip6f-15-s-book/ip6-snooping.pdf
NEW QUESTION 125
Refer to the exhibit.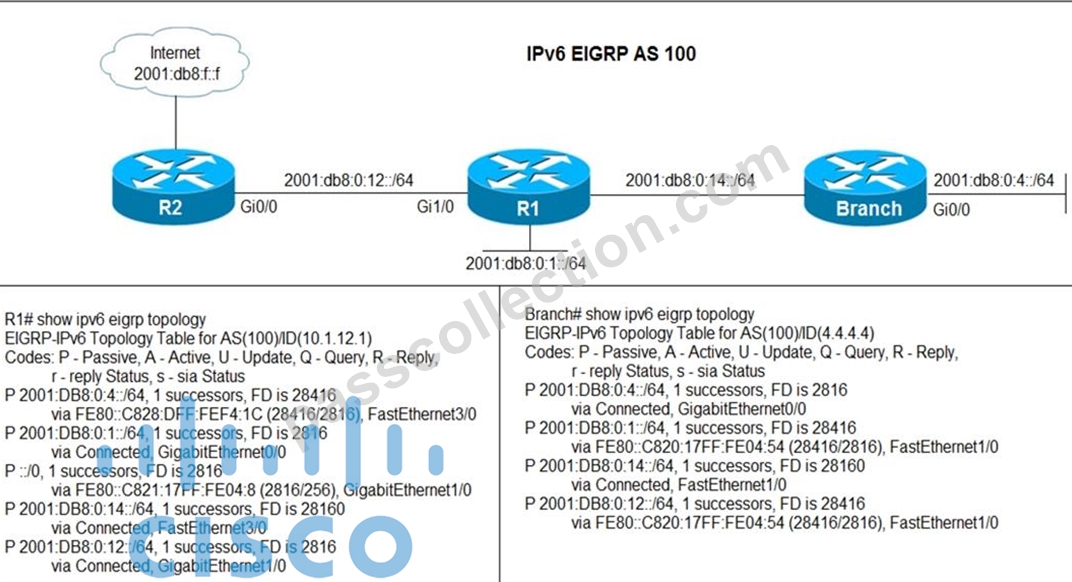
Users in the branch network of 2001:db8:0:4::/64 report that they cannot access the Internet. Which command is issued in IPv6 router EIGRP 100 configuration mode to solve this issue?
- A. Issue the no eigrp stub command on R1.
- B. Issue the eigrp stub command on R2.
- C. Issue the no eigrp stub command on R2.
- D. Issue the eigrp stub command on R1.
Answer: D
NEW QUESTION 126
R2 has a locally originated prefix 192.168.130.0/24 and has these configurations: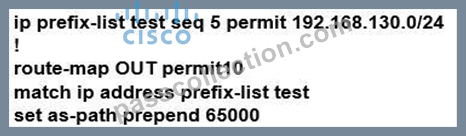
What is the result when the route-map OUT command is applied toward an eBGP neighbor R1 (1.1.1.1) by using the neighbor 1.1.1.1 route-map OUT out command?
- A. R1 does not forward traffic that is destined for 192.168.30.0/24
- B. Network 192.168.130.0/24 is not allowed in the R1 table
- C. R1 does not accept any routes other than 192.168.130.0/24
- D. R1 sees 192.168.130.0/24 as two AS hops away instead of one AS hop away.
Answer: D
NEW QUESTION 127
Refer to the exhibit.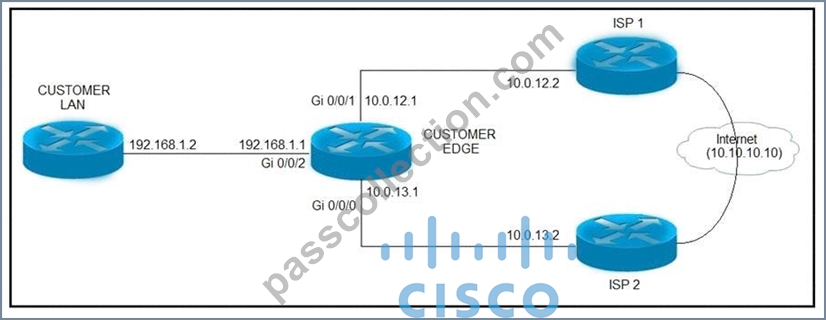
ISP 1 and ISP 2 directly connect to the Internet. A customer is tracking both ISP links to achieve redundancy and cannot see the Cisco IOS IP SLA tracking output on the router console. Which command is missing from the IP SLA configuration?
- A. Start-time 00:00
- B. Start-time immediately
- C. Start-time 0
- D. Start-time now
Answer: D
NEW QUESTION 128
An engineer configured policy-based routing for a destination IP address that does not exist in the routing table. How is the packet treated through the policy for configuring the set ip default next-hop command?
- A. Packets are not forwarded to the specific next hop.
- B. Packets are forwarded based on the routing table.
- C. Packets are forwarded to the specific next hop.
- D. Packets are forwarded based on a static route.
Answer: C
NEW QUESTION 129
Refer to the exhibit.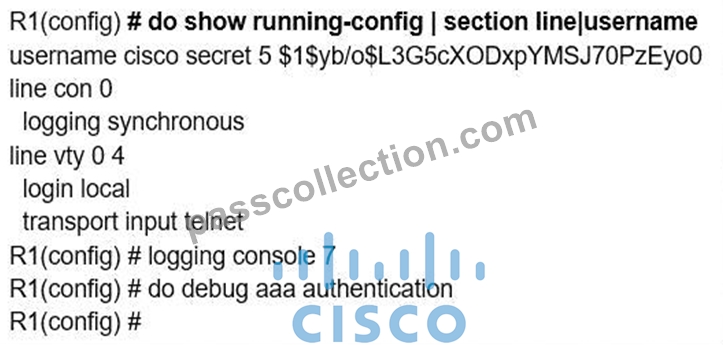
An administrator that is connected to the console does not see debug messages when remote users log in. Which action ensures that debug messages are displayed for remote logins?
- A. Enter the transport input ssh configuration command.
- B. Enter the logging console debugging configuration command.
- C. Enter the terminal monitor exec command.
- D. Enter the aaa new-model configuration command.
Answer: B
Explanation:
Explanation
The logging console is a default and hidden command.
NEW QUESTION 130
What are two functions of MPLS Layer 3 VPNs? (Choose two.)
- A. A packet with node segment ID is forwarded along with shortest path to destination.
- B. BGP is used for signaling customer VPNv4 routes between PE nodes.
- C. It is used for transparent point-to-multipoint connectivity between Ethernet links/sites.
- D. Customer traffic is encapsulated in a VPN label when it is forwarded in MPLS network.
- E. LDP and BGP can be used for Pseudowire signaling.
Answer: B,D
NEW QUESTION 131
Refer to the exhibit.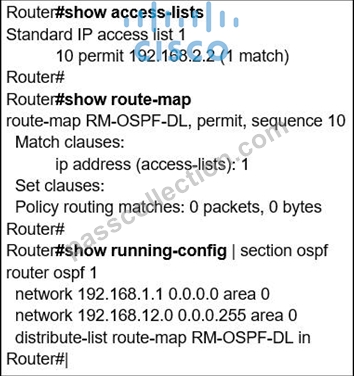
An engineer is trying to block the route to 192.168.2.2 from the routing table by using the configuration that is shown. The route is still present in the routing table as an OSPF route. Which action blocks the route?
- A. Use an extended access list instead of a standard access list.
- B. Use a prefix list instead of an access list in the route map.
- C. Add this statement to the route map: route-map RM-OSPF-DL deny 20.
- D. Change sequence 10 in the route-map command from permit to deny.
Answer: B
NEW QUESTION 132
After some changes in the routing policy, it is noticed that the router in AS 45123 is being used as a transit AS router for several service provides. Which configuration ensures that the branch router in AS 45123 advertises only the local networks to all SP neighbors?
A)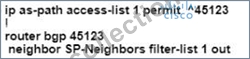
B)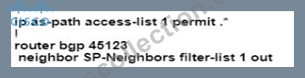
C)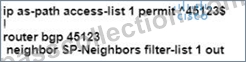
D)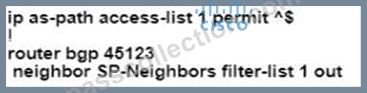
- A. Option A
- B. Option D
- C. Option B
- D. Option C
Answer: B
NEW QUESTION 133
While working with software images, an engineer observes that Cisco DNA Center cannot upload its software image directly from the device.
Why is the image not uploading?
- A. The software image for the device is in install mode.
- B. The device must be resynced to Cisco DNA Center.
- C. The device has lost connectivity to Cisco DNA Center.
- D. The software image for the device is in bundle mode
Answer: A
Explanation:
Section: Infrastructure Services
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/cloud-systems-management/network-automation-and- management/dna-center/1-2-10/user_guide/b_cisco_dna_center_ug_1_2_10/ b_dnac_ug_1_2_10_chapter_0100.html
NEW QUESTION 134
An engineer configured a leak-map command to summarize EIGRP routes and advertise specifically loopback 0 with an IP of 10.1.1.1.255.255.255.252 along with the summary route. After finishing configuration, the customer complained not receiving summary route with specific loopback address. Which two configurations will fix it? (Choose two.)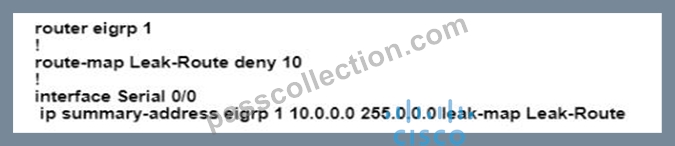
- A. Configure route-map Leak-Route permit 20.
- B. Configure access-list 1 and match under route-map Leak-Route.
- C. Configure access-list 1 permit 10.1.1.0.0.0.0.3.
- D. Configure access-list 1 permit 10.1.1.1.0.0.0.252.
- E. Configure route-map Leak-Route permit 10 and match access-list 1.
Answer: C,E
Explanation:
When you configure an EIGRP summary route, all networks that fall within the range of your summary are suppressed and no longer advertised on the interface. Only the summary route is advertised. But if we want to advertise a network that has been suppressed along with the summary route then we can use leak-map feature. The below commands will fix the configuration in this question:
R1(
config)#access-list 1 permit 10.1.1.0 0.0.0.3
R1(config)#route-map Leak-Route permit 10 // this command will also remove the "route_map Leak-Route deny 10" command.
R1(config-route-map)#match ip address 1
NEW QUESTION 135
Drag and drop the LDP features from the left onto the descriptions on the right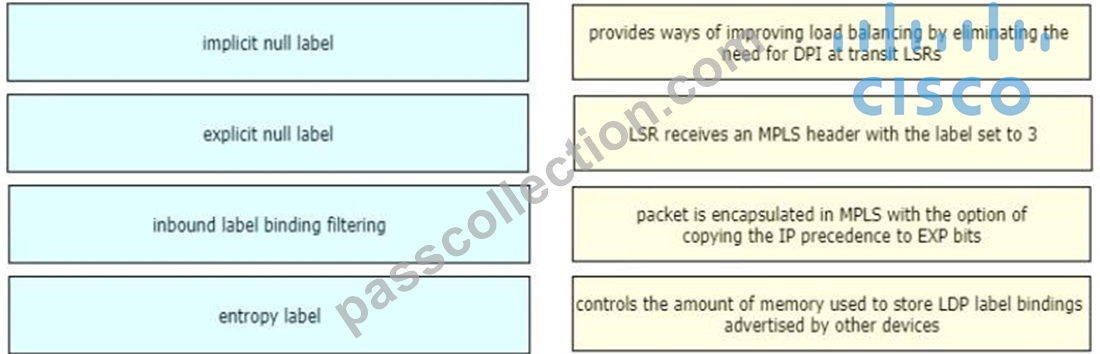
Answer:
Explanation: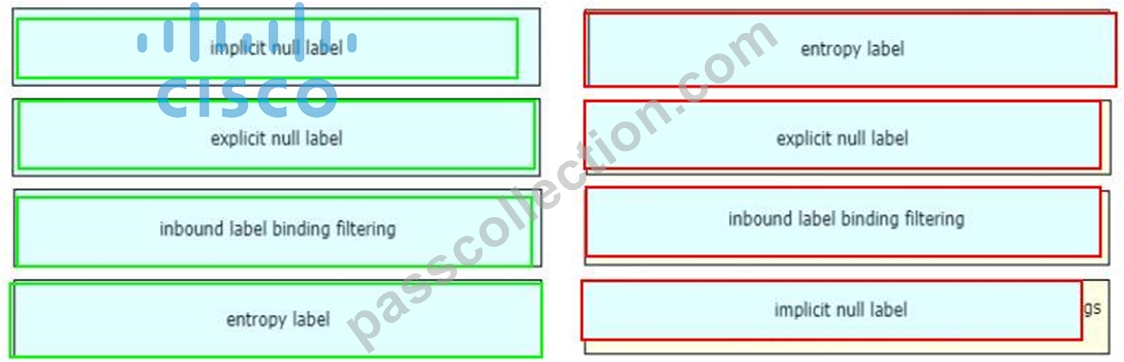
NEW QUESTION 136
After some changes in the routing policy, it is noticed that the router in AS 45123 is being used as a transit AS router for several service provides. Which configuration ensures that the branch router in AS 45123 advertises only the local networks to all SP neighbors?
A)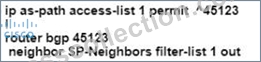
B)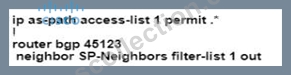
C)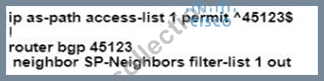
D)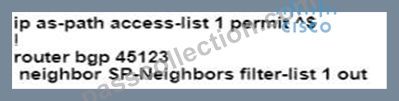
- A. Option A
- B. Option D
- C. Option B
- D. Option C
Answer: B
NEW QUESTION 137
Which command allows traffic to load-balance in an MPLS Layer 3 VPN configuration?
- A. multi-paths 2
- B. maximum-paths ibgp 2
- C. multi-paths eibgp 2
- D. maximum-paths 2
Answer: B
Explanation:
Section: VPN Technologies
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/switches/datacenter/sw/5_x/nx-os/mpls/configuration/guide/ mpls_cg/mp_vpn_multipath.html
NEW QUESTION 138
Refer to the exhibit.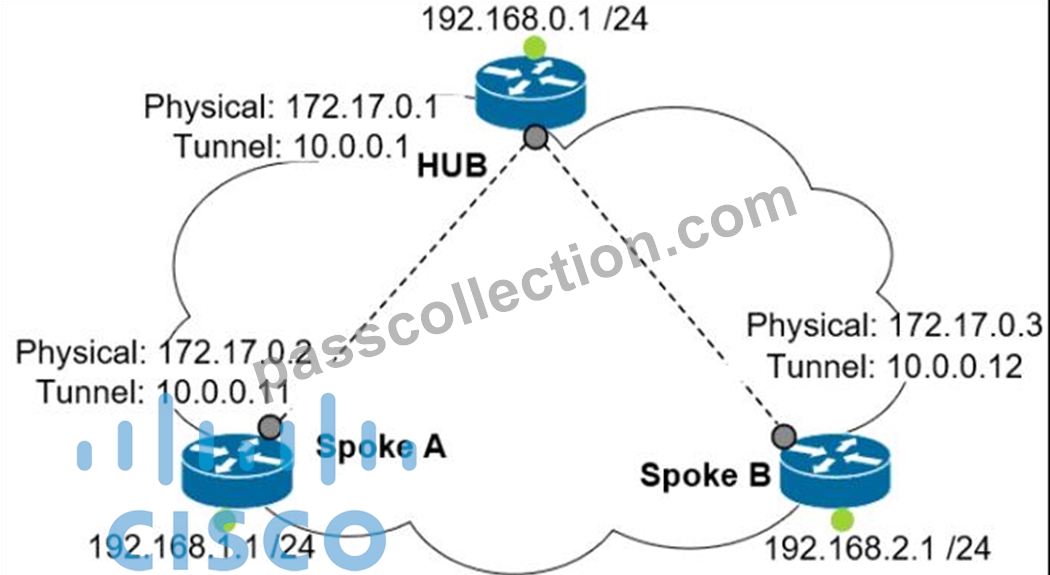
Which interface configuration must be configured on the spoke A router to enable a dynamic DMVPN tunnel with the spoke B router?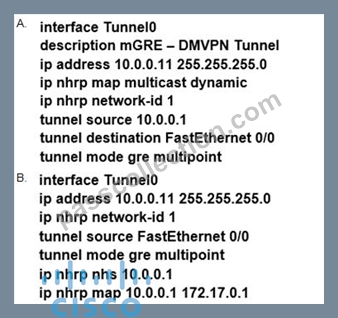
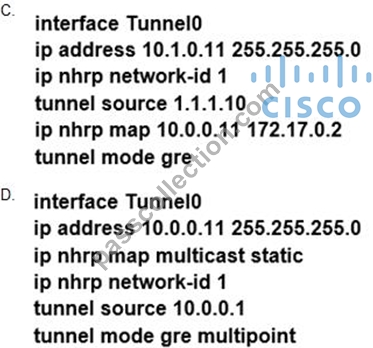
- A. Option D
- B. Option B
- C. Option A
- D. Option C
Answer: B
NEW QUESTION 139
Refer to the exhibit.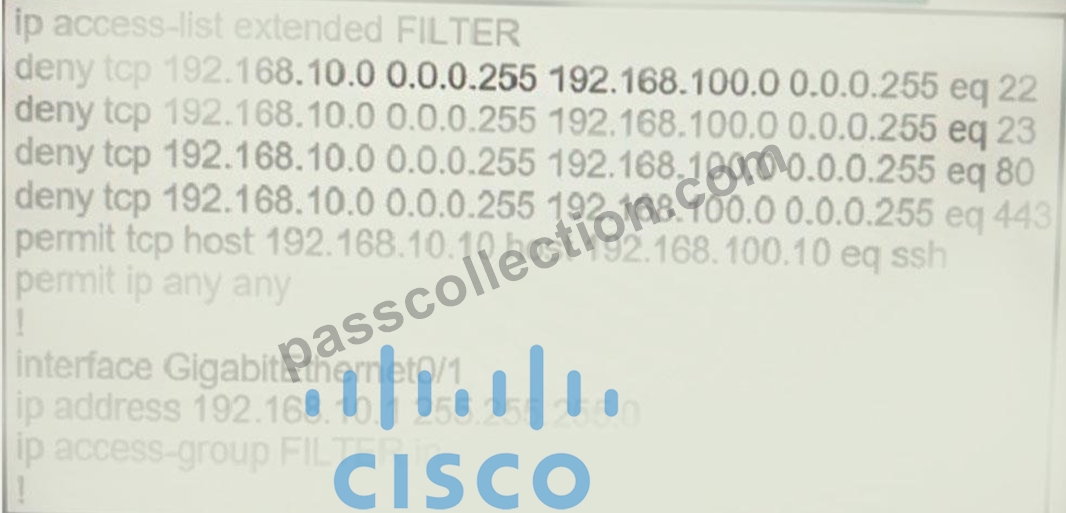
The ACL is placed on the inbound Gigabit 0/1 interface of the router. Host
192.168.10.10cannot SSH to host 192.168.100.10 even though the flow is permitted. Which action resolves the issue without opening full access to this router?
- A. Temporarily remove the ACL from the interface to see if the flow works
- B. Temporarily move the permit ip any any line to the beginning of the ACL to see if the flow works
- C. Run the show access-list FILTER command to view if the SSH entry has any hit statistic associated with it
- D. Move the SSH entry to the beginning of the ACL
Answer: D
NEW QUESTION 140
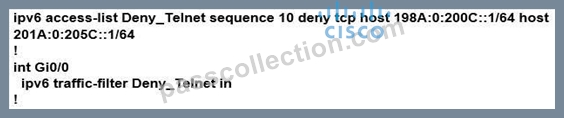
Refer to the exhibit. Which configuration denies Telnet traffic to router 2 from 198A:0:200C::1/64?
- A.
- B.
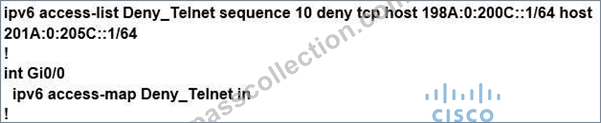
- C.
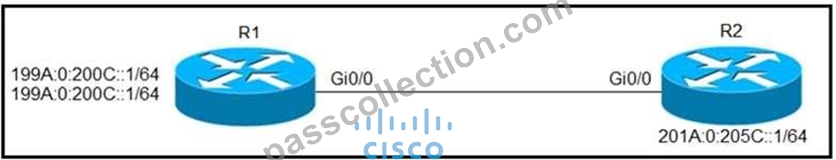
- D.
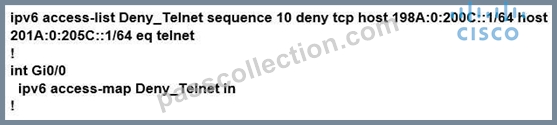
- E.
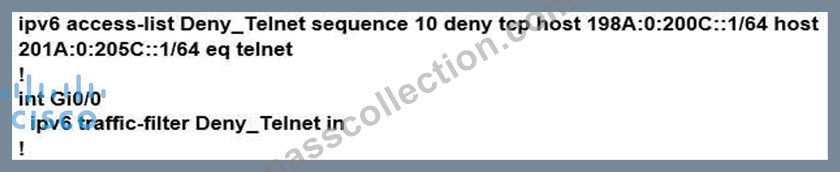
Answer: C
Explanation:
Section: Infrastructure Security
NEW QUESTION 141
Which transport layer protocol is used to form LDP sessions?
- A. SCTP
- B. TCP
- C. RDP
- D. UDP
Answer: B
Explanation:
LDP multicasts hello messages to a well-known UDP port (646) in order to discover neighbors. Once the discovery is accomplished, a TCP connection (port 646) is established and the LDP session begins. LDP keepalives ensure the health of the session. Thanks to the LDP session, LDP messages create the label mappings required for a FEC. Withdraw messages are used when FECs need to be torn down.
NEW QUESTION 142
Refer to the exhibit.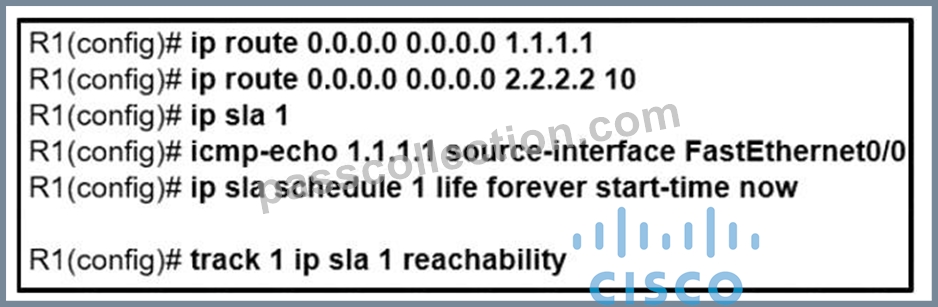
An IP SLA is configured to use the backup default route when the primary is down, but it is not working as desired. Which command fixes the issue?
- A. R1(config)# ip route 0.0.0.0.0.0.0.0.2.2.2.2
- B. R1(config)#ip sla track 1
- C. R1(config)# ip route 0.0.0.0.0.0.0.0.2.2.2.2 10 track 1
- D. R1(config)# ip route 0.0.0.0.0.0.0.0.1.1.1.1 track 1
Answer: D
NEW QUESTION 143
Drag and Drop the IPv6 First-Hop Security features from the left onto the definitions on the right.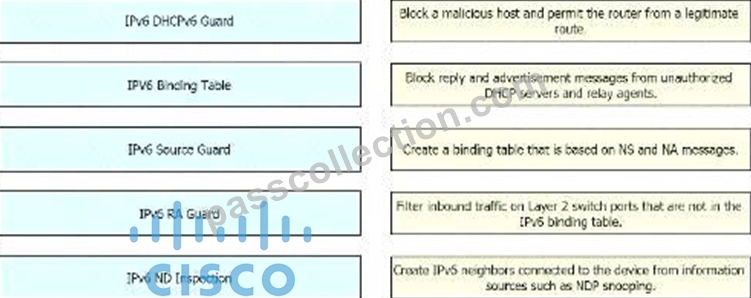
Answer:
Explanation: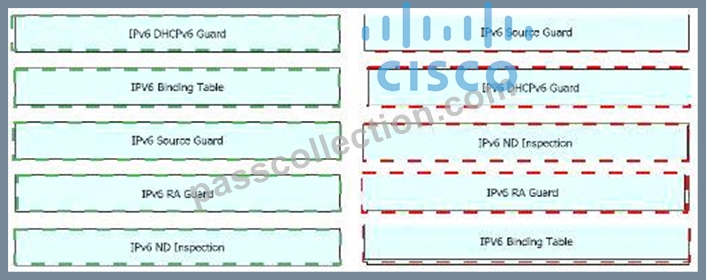
NEW QUESTION 144
Refer to the exhibit.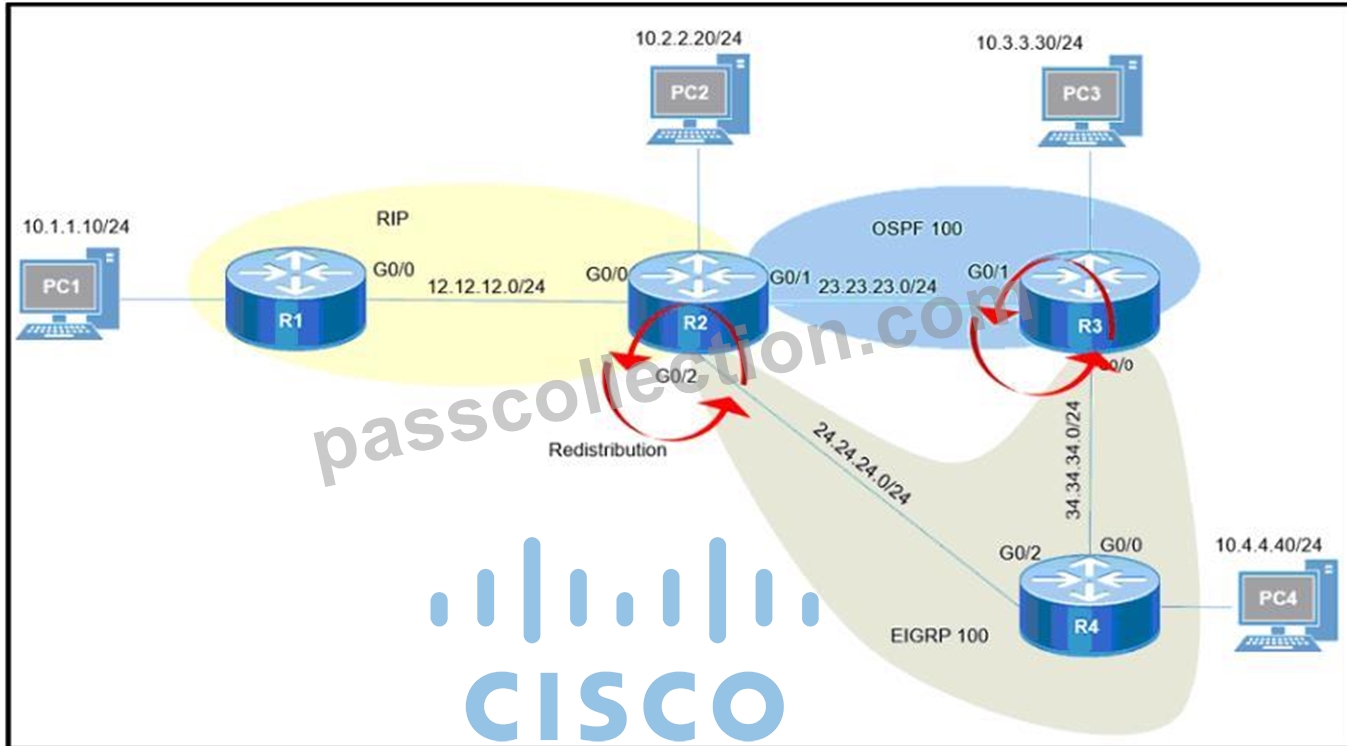
Redistribution is enabled between the routing protocols, and nowPC2 PC3, and PC4 cannot reach PC1. What are the two solutions to fix the problem? (Choose two.)
- A. Filter all routes except EIGRP routes when redistributing into OSPF in R3.
- B. Filter all routes except RIP routes when redistributing into EIGRP in R2.
- C. Filter OSPF routes into RIP FROM EIGRP when redistributing into RIP in R2.
- D. Filter RIP AND OSPF routes back into OSPF from EIGRP when redistributing into OSPF in R2
- E. Filter RIP routes back into RIP when redistributing into RIP in R2
Answer: C,E
Explanation:
Explanation
Even PC2 cannot reach PC1 so there is something wrong with RIP redistribution in R2. Because RIP has higher Administrative Distance (AD) value than OSPF and EIGRP so it will be looped when doing mutual redistribution.
NEW QUESTION 145
What are two functions of IPv6 Source Guard? (Choose two.)
- A. It works independent from IPv6 neighbor discovery.
- B. It blocks certain traffic by inspecting DHCP packets for specific sources.
- C. It uses the populated binding table for allowing legitimate traffic.
- D. It denies traffic by inspecting neighbor discovery packets for specific pattern.
- E. It denies traffic from unknown sources or unallocated addresses.
Answer: C,E
NEW QUESTION 146
......
Online Questions - Outstanding Practice To your 300-410 Exam: https://www.passcollection.com/300-410_real-exams.html
Practice To 300-410 - PassCollection Remarkable Practice On your Implementing Cisco Enterprise Advanced Routing and Services Exam: https://drive.google.com/open?id=1pWz8-GzCywx7a3ZBRIxukdBUNsUZ1UC8
