

Prepare Important Exam with NSE6_FSM_AN-7.4 Exam Dumps(2026)
Pass Exam Questions Efficiently With NSE6_FSM_AN-7.4 Questions
NEW QUESTION # 15
You need a model that predicts a target field based on other fields in a dataset and then triggers an anomaly if the value does not match the prediction. Which machine learning (ML) algorithm will you use to build this type of model?
- A. Forecasting
- B. Regression
- C. Anomaly detection
- D. Classification
Answer: B
Explanation:
Regression models predict the value of a target field using other fields as predictors. FortiSIEM can then generate anomalies when the observed value significantly deviates from the predicted value.
NEW QUESTION # 16
Refer to the exhibit. Which two actions can you select in an automation policy to trigger an API call to block an IP address on a FortiGate? (Choose two.)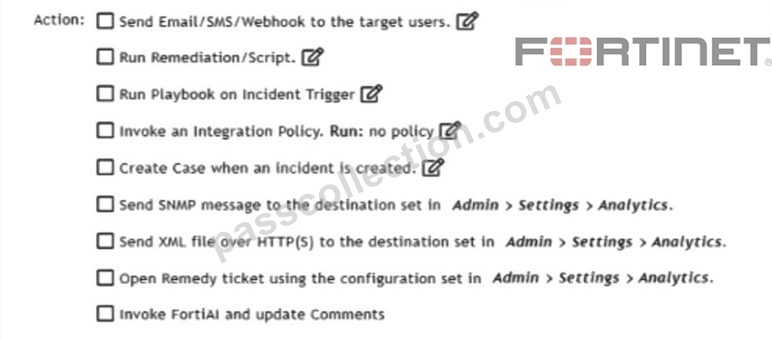
- A. Run Playbook on Incident Trigger
- B. Send Email/SMS/Webhook to the target users
- C. Run Remediation/Script
- D. Open Remedy ticket using the configuration set in
- E. Invoke an Integration Policy
Answer: C,E
Explanation:
An automation policy can trigger an API-based response by invoking an integration policy or by running a remediation script. Both methods can be used to perform automated response actions such as calling the FortiGate API to block a malicious IP address.
NEW QUESTION # 17
Refer to the exhibit.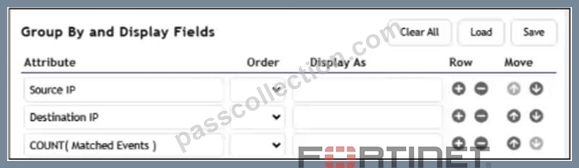
If you apply this Group By and Display Fields configuration to a list of network connections, which information will FortiSIEM display?
- A. A running count of connections, regardless of their source and destination
- B. A list of connections between unique source and destination IP addresses
- C. A list of connections ordered by the total amount of data sent between unique devices
- D. A list of connections ordered by the number of unique connections started by each unique source IP address
Answer: B
Explanation:
Grouping by Source IP and Destination IP causes FortiSIEM to aggregate events into unique source-to-destination connection pairs. The matched-events count is displayed for each unique pair, showing how many connections or matching events exist for that grouped relationship.
NEW QUESTION # 18
From which two sources can you import data to train FortiSIEM machine learning? (Choose two.)
- A. CSV files
- B. Syslog archives
- C. SQL database
- D. FortiSIEM reports
Answer: A,D
NEW QUESTION # 19
Refer to the exhibit.
The configuration for a machine learning (ML) dataset using anomaly detection is shown.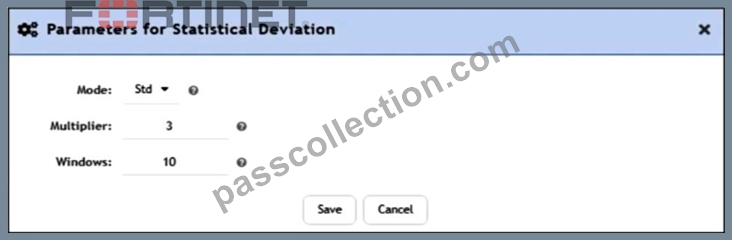
If data for this model is generated every hour, how long must the FortiSIEM device be up before it can produce a valid training set?
- A. 30 hours
- B. 10 hours
- C. 3 hours
- D. 24 hours
Answer: B
Explanation:
The Windows parameter is set to 10, meaning FortiSIEM requires 10 data windows to build a valid training baseline. Since data is generated every hour, the device must collect 10 hours of data before producing a valid training set.
NEW QUESTION # 20
A critical server is sending traffic that is triggering a high severity outbound intrusion prevention system (IPS) permitted IPS exploit rule. This traffic must be allowed. Which two items must you configure to prevent this sever from triggering the incident? (Choose two.)
- A. Modify the aggregate count in the subpattern.
- B. Modify the subpattern filter to exclude the IP address.
- C. Change the time window on the rule conditions.
- D. Create a rule exception for the IP address.
- E. Modify the group by parameters to exclude the IP address.
Answer: B,D
Explanation:
To stop a known allowed server from generating this incident, you can tune the rule logic by excluding the server IP address in the subpattern filter. You can also create a rule exception for that IP address, which suppresses incident generation for matching traffic from the approved server while leaving the rule active for other sources.
NEW QUESTION # 21
An analyst wants to create a rule from a new analytic search they just performed. Which method is the most efficient way for you to create the rule?
- A. Save the search as a template, and create a new rule from the template.
- B. Copy and paste the raw analytics search text into a rule subpattern.
- C. Manually re-create the analytics search in the rule configuration.
- D. Make a new rule using the Create Rule option in the Actions menu.
Answer: D
Explanation:
Using the Create Rule option directly from the Actions menu is the most efficient method because it automatically converts the existing analytic search into a rule structure without requiring manual reconfiguration.
NEW QUESTION # 22
Refer to the exhibit.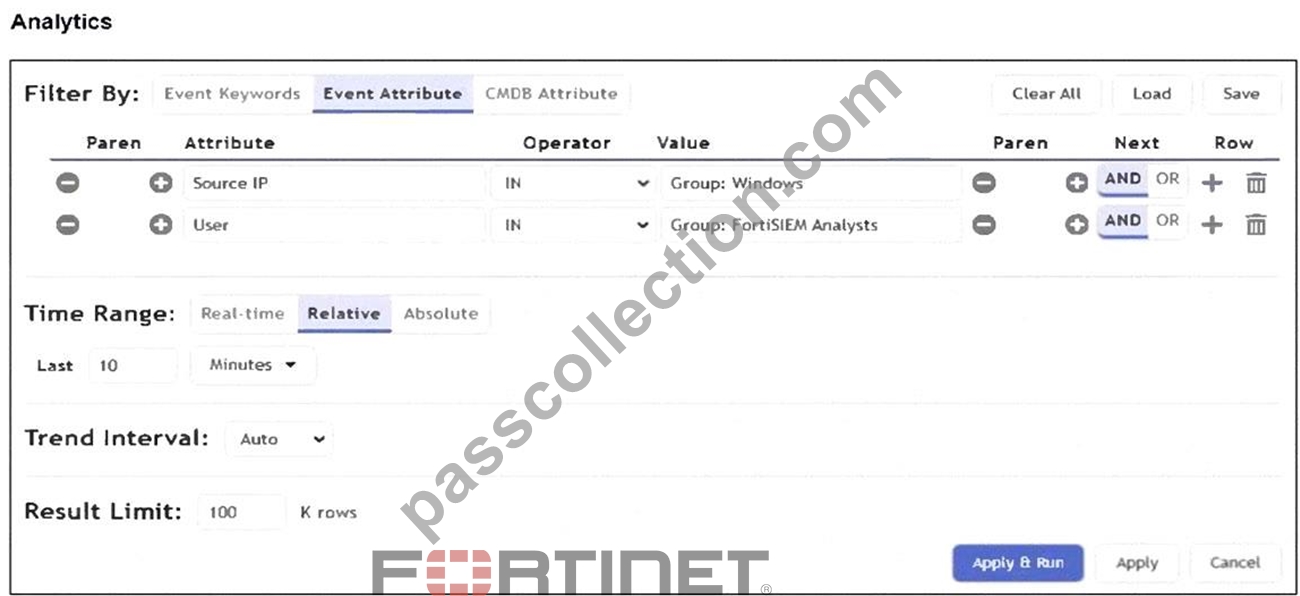
What is the Group: FortiSIEM Analysts value referring to?
- A. CMDB user group
- B. Windows Active Directory user group
- C. FortiSIEM organization group
- D. LDAP user group
Answer: A
Explanation:
The correct answer is C. CMDB user group . In FortiSIEM, users and user groups are maintained as CMDB objects and can be referenced in analytics filters and rule logic. The FortiSIEM 7.4 User Guide table of contents explicitly includes CMDB management for users, viewing user information, adding users, editing or deleting users, performing operations on users, and working with user groups. This confirms that user groups are part of the FortiSIEM CMDB data model. The query shown in the exhibit uses the Analytics filter with the User attribute and the value Group: FortiSIEM Analysts . That syntax indicates that FortiSIEM is referencing a FortiSIEM-defined user group from CMDB, not an LDAP group directly and not an Active Directory group directly. LDAP and Active Directory can be used to discover or authenticate users, but once referenced as a FortiSIEM analytics group value, the object is a CMDB user group. FortiSIEM organization groups are tenant/organization constructs and are not the same as CMDB user groups.
NEW QUESTION # 23
You want to build an event query that displays only events to higher number destination ports (1024-65535). Which analytic search string is valid for this scenario?
- A. Destination TCP/UDP Port >= 1024 AND Destination TCP/UDP Port <= 65535
- B. Destination TCP/UDP Port BETWEEN 1024-65535
- C. Destination TCP/UDP Port > 1024
- D. Destination TCP/UDP Port = 1024-65535
Answer: A
Explanation:
FortiSIEM analytic searches support explicit comparison operators. Using greater-than-or-equal- to and less-than-or-equal-to conditions correctly defines the valid destination port range from
1024 through 65535.
NEW QUESTION # 24
Refer to the exhibit.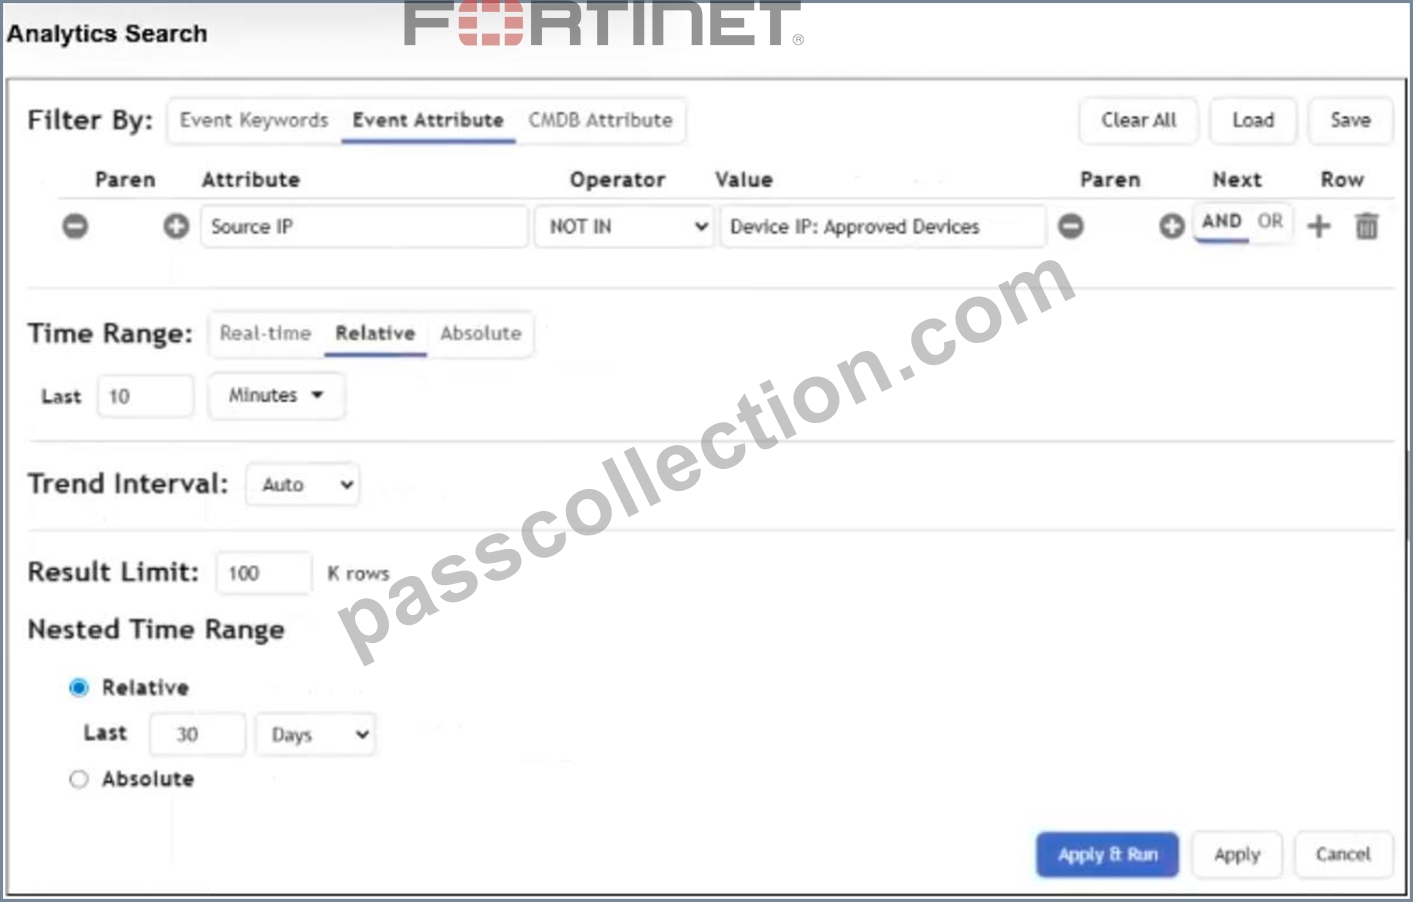
Which statement about the time range settings defined in the nested query is accurate?
- A. FortiSIEM will search in real time using 10 minute blocks for a source IP address that is not in the Approved Devices report from the last 30 days.
- B. FortiSIEM will list source IP addresses found the last 10 minutes of events from each day in the Approved Devices report from the last 30 days.
- C. FortiSIEM will search the last 30 days of events for a source IP address that is not in the Approved Devices report.
- D. FortiSIEM will search the last 10 minutes of events for a source IP address that is not in the Approved Devices report from the last 30 days.
Answer: D
Explanation:
The main analytics search uses the last 10 minutes as the event time range. The nested query uses the Approved Devices report generated from the last 30 days, so FortiSIEM compares recent source IP addresses against that 30-day approved-device result set.
NEW QUESTION # 25
Refer to the exhibit. What is the Group: VPN Gateway value referring to?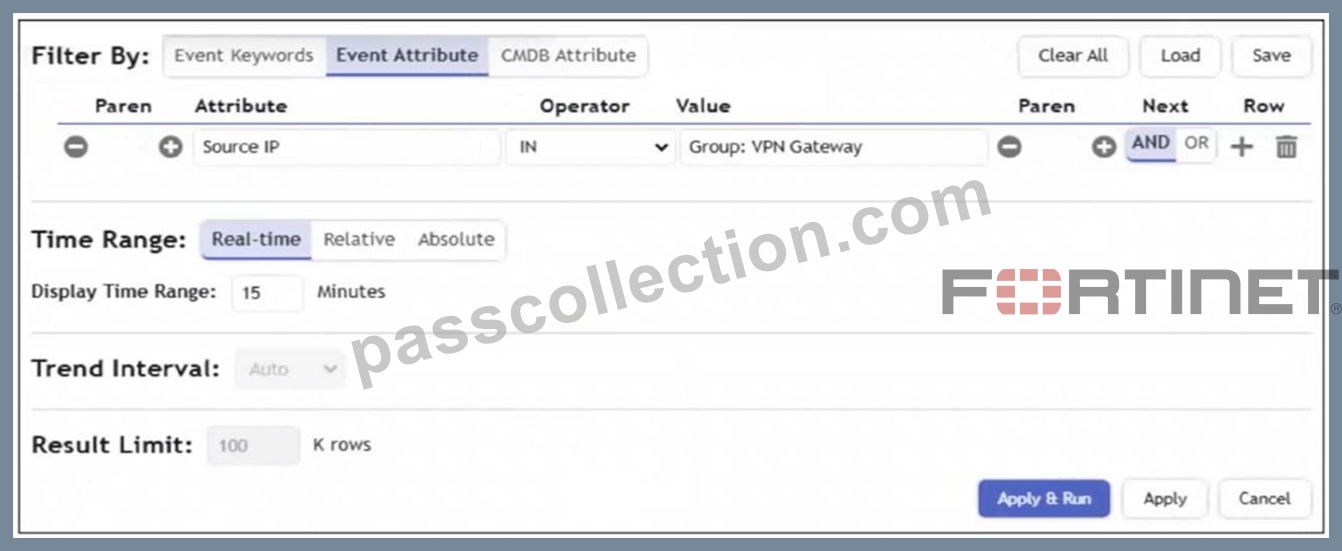
- A. A watchlist
- B. A FortiGate address group
- C. An authentication user group
- D. A CMDB device group
Answer: D
Explanation:
The value Group: VPN Gateway refers to a CMDB device group in FortiSIEM. This group represents a collection of devices categorized as VPN Gateways in the Configuration Management Database. By filtering with this group, the query retrieves events where the Source IP matches any device included in the CMDB group "VPN Gateway."
NEW QUESTION # 26
Refer to the exhibit. Which event type attribute value will the FortiSIEM parser save for this event?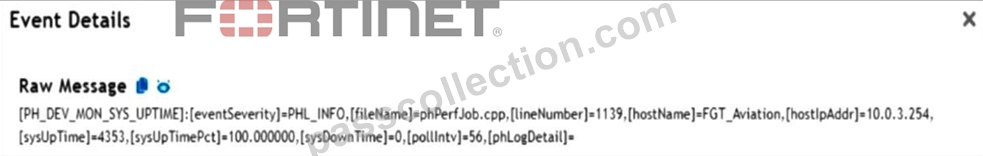
- A. sysUpTime
- B. phLogDetail
- C. PHL_INFO
- D. PH_DEV_MON_SYS_UPTIME
Answer: D
Explanation:
FortiSIEM parsers map raw event attributes to normalized event type attributes. In this event, the parser identifies the sysUpTime value and stores it under the normalized FortiSIEM attribute name PH_DEV_MON_SYS_UPTIME.
NEW QUESTION # 27
When configuring machine learning (ML), in which step can you modify how the model fits the training data set?
- A. Prepare Data
- B. Design
- C. Statistics
- D. Train
Answer: C
Explanation:
The Statistics step is where you tune statistical model parameters that affect how closely the machine learning model fits the training data set, such as deviation-related settings used for anomaly detection.
NEW QUESTION # 28
In an automation policy, which two methods can you use to notify analysts when an incident is triggered? (Choose two.)
- A. FortiSIEM Case
- B. Pop-up window
- C. Syslog
- D. Email
Answer: A,D
NEW QUESTION # 29
Refer to the exhibit. According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?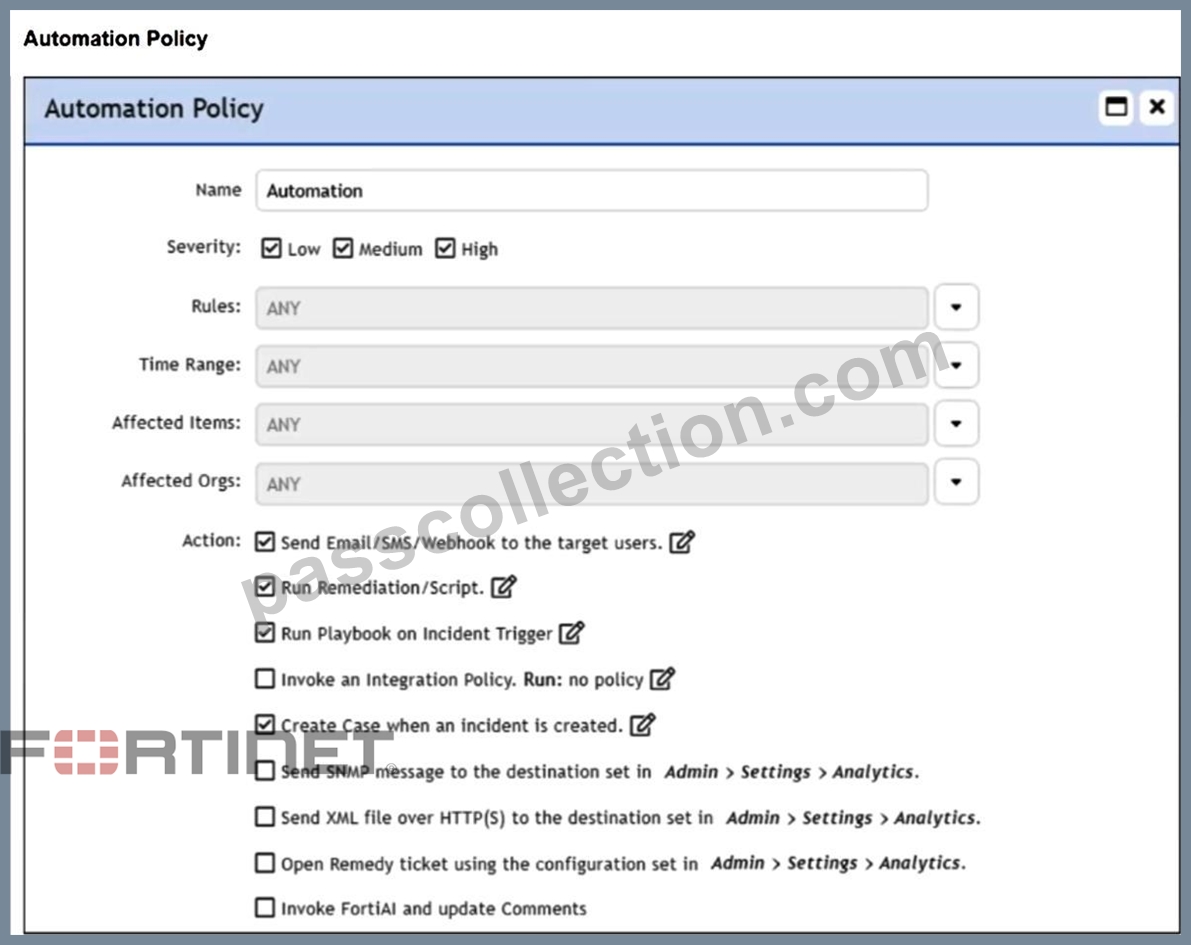
- A. FortiSIEM executes all the actions.
- B. FortiSIEM runs everything except the playbook, because the playbook and the remediation script perform similar functions.
- C. FortiSIEM runs the remediation script.
- D. FortiSIEM sends an email.
Answer: A
Explanation:
All selected actions in the automation policy are executed when the associated rule triggers. In this configuration, email/webhook notification, remediation/script execution, playbook execution, and case creation are all enabled.
NEW QUESTION # 30
Refer to the exhibit.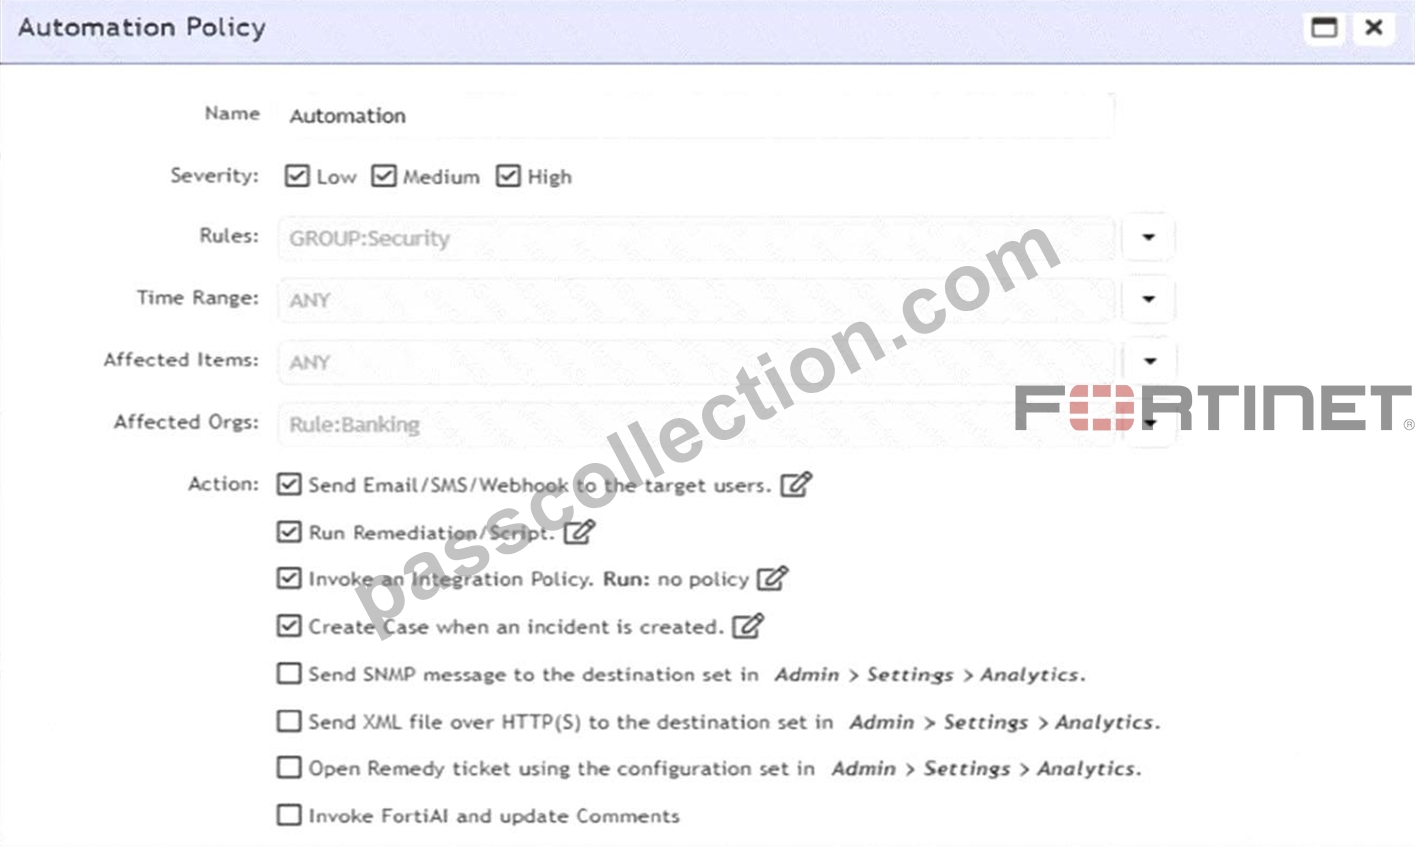
According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?
- A. FortiSIEM runs the remediation script, because that takes precedence over all other options.
- B. FortiSIEM fails to the integration policy, because no policy is defined.
- C. FortiSIEM sends an email, because that is first on the list.
- D. FortiSIEM performs all selected actions.
Answer: D
Explanation:
When an associated rule triggers, FortiSIEM performs all selected actions in the automation policy. In this case, it will send an email/SMS/webhook, run the remediation script, invoke the integration policy (even if none is currently defined), and create a case. All checked actions are executed.
The correct answer is B because FortiSIEM automation policies are designed to execute the actions selected in the policy when the policy criteria match. The FortiSIEM Study Guide states that automation policy actions define what occurs when policy criteria match. It lists possible automation actions such as sending an alert, invoking an integration policy, sending SNMP or HTTPS XML notifications, opening a remedy ticket or creating a FortiSIEM case, sending email or SMS, and running a remediation script. The same Study Guide explains that users can configure "any combination of actions." Therefore, there is no single-action precedence rule where remediation overrides all other selected actions or email runs only because it appears first. If multiple action checkboxes are selected, FortiSIEM executes the configured selected actions according to the automation policy. In the exhibit, multiple actions are selected, including email/SMS
/webhook, remediation/script, integration policy, and case creation. Option C is incorrect because the absence of a defined integration policy does not make FortiSIEM ignore the other selected actions. The policy runs the selected configured actions.
NEW QUESTION # 31
Refer to the exhibit.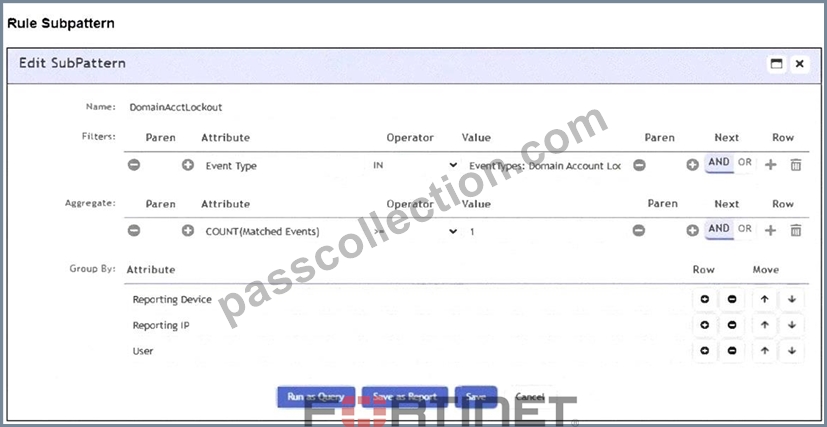
Which section contains the subpattern configuration that determines how many matching events are needed to trigger the rule?
- A. Aggregate
- B. Actions
- C. Group By
- D. Filters
Answer: A
Explanation:
The Aggregate section contains the condition COUNT(Matched Events) > = 1, which defines how many events must match the filter criteria for the rule to trigger. This is the subpattern configuration that determines the event threshold.
The correct answer is A. Aggregate . In FortiSIEM rule subpatterns, the Filter section defines which events are eligible for matching, but the Aggregate section defines the statistical or threshold condition that must be satisfied before the subpattern is considered matched. The Study Guide explains that rule conditions are built from subpatterns of event attribute filters and aggregation functions. It also states that a single-subpattern rule is formed by three fields: filters, aggregate, and group by. In the exhibit, the aggregate line is COUNT (Matched Events) > = 1. That expression directly specifies the number of matching events required to satisfy the subpattern. Group By only controls how matching events are partitioned into separate evaluation groups.
Actions define what happens after a rule triggers, such as incident generation or notification. Filters define the event type or attribute criteria, but they do not define the required count threshold. Therefore, the section that determines how many matching events are needed is the Aggregate section.
NEW QUESTION # 32
Refer to the exhibit.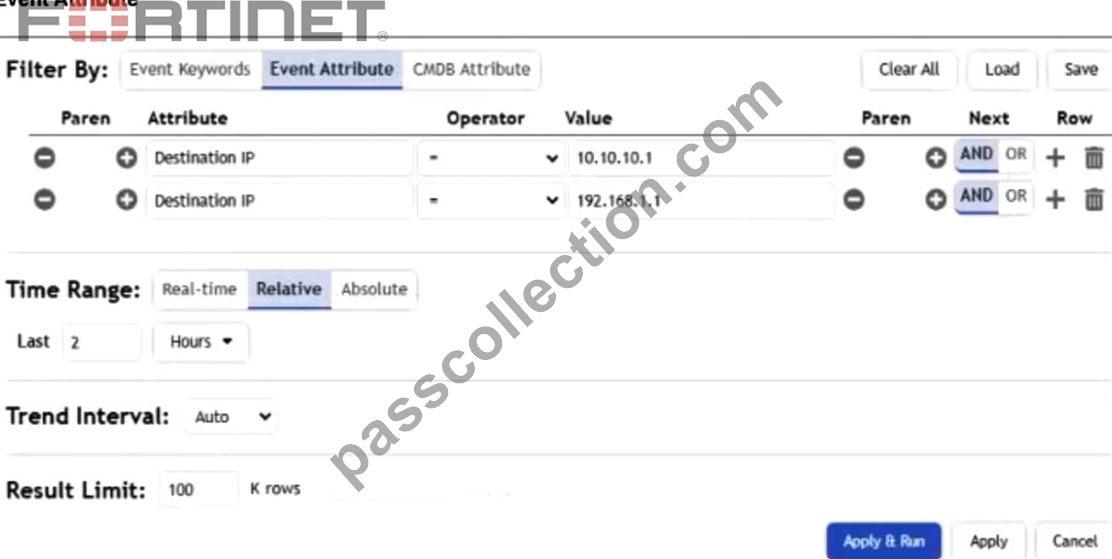
You are investigating an issue with two destination IP addresses, but you are not getting any results from the search.
Based on the filters shown in the exhibit, why is this search returning no results?
- A. You are using an invalid IP address in the Value column.
- B. You are using an incorrect entry in the Operator column.
- C. The two items are not grouped in parentheses ().
- D. You are using the wrong Boolean operator in the Next column.
Answer: D
Explanation:
The search is using an AND condition between two different values for the same Destination IP attribute. A single event cannot have both destination IP addresses at the same time, so the filter returns no results. The condition should use OR to search for events matching either destination IP address.
NEW QUESTION # 33
Refer to the exhibit. If you group the events by Reporting IP, Event Type, and User attributes, how many results will FortiSIEM display?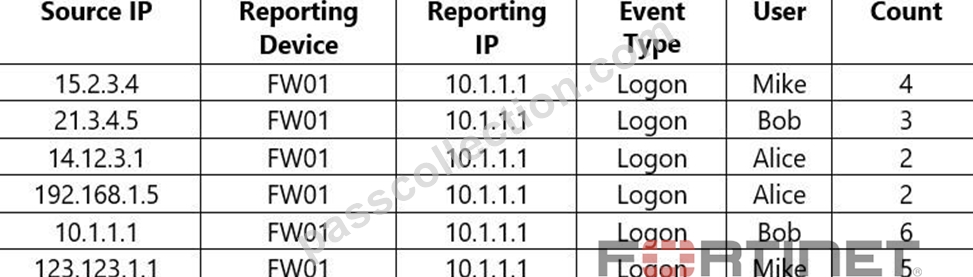
- A. Three
- B. Five
- C. Two
- D. Four
Answer: A
Explanation:
When grouped by Reporting IP, Event Type, and User, FortiSIEM consolidates rows sharing the same values for these attributes.
Reporting IP: all are 10.1.1.1
Event Type: all are Logon
Users: Mike, Bob, and Alice
Thus, FortiSIEM will display three results, one for each user.
NEW QUESTION # 34
Refer to the exhibits.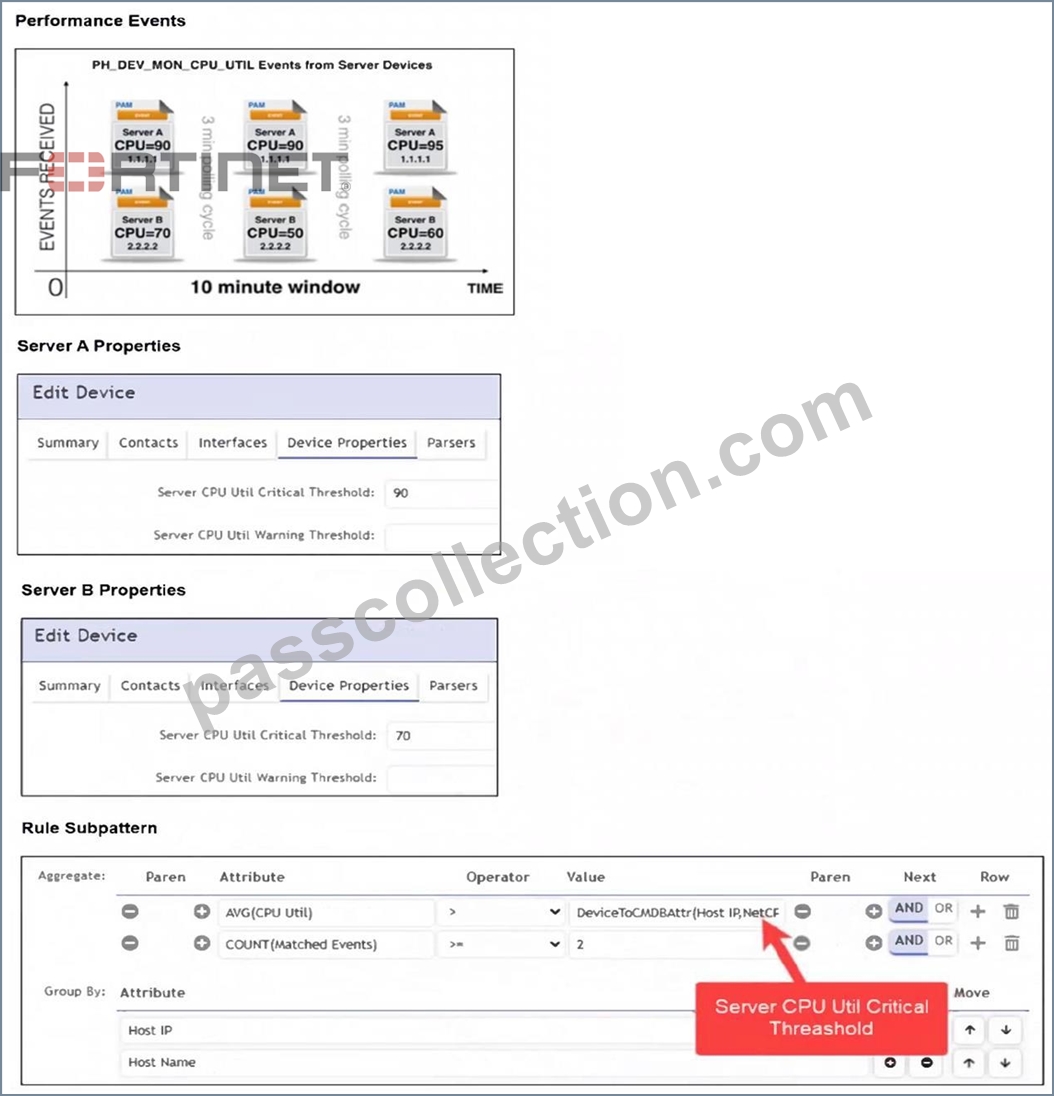
Three events are collected over 10 minutes from two servers: Server A and Server B.
Based on the settings for the rule subpattern and a 10-minute condition window, how many incidents will the servers generate?
- A. Server A will generate one incident and Server B will generate one incident.
- B. Server A will generate one incident and Server B will not generate any incidents.
- C. Server A will not generate any incidents and server B will generate one incident.
- D. Server A will not generate any incidents and Server B will not generate any incidents.
Answer: B
Explanation:
The rule triggers when the average CPU utilization (AVG(CPU Util)) exceeds the device's CMDB critical threshold and there are at least two matching events within the 10-minute window.
Server A: Average CPU = (90 + 95) / 2 = 92.5, which is greater than its critical threshold of 90, and it has two events, so one incident is generated.
Server B: Average CPU = (70 + 60) / 2 = 65, which is below its critical threshold of 70, so no incident is generated.
So, Server A generates one incident, and Server B generates none.
NEW QUESTION # 35
You need a model that predicts a target field based on other fields in a dataset and then triggers an anomaly if the value does not match the prediction. Which machine learning (ML) algorithm will you use to build this type of model?
- A. Forecasting
- B. Regression
- C. Anomaly detection
- D. Classification
Answer: B
NEW QUESTION # 36
Refer to the exhibit. Why is this search not producing any results?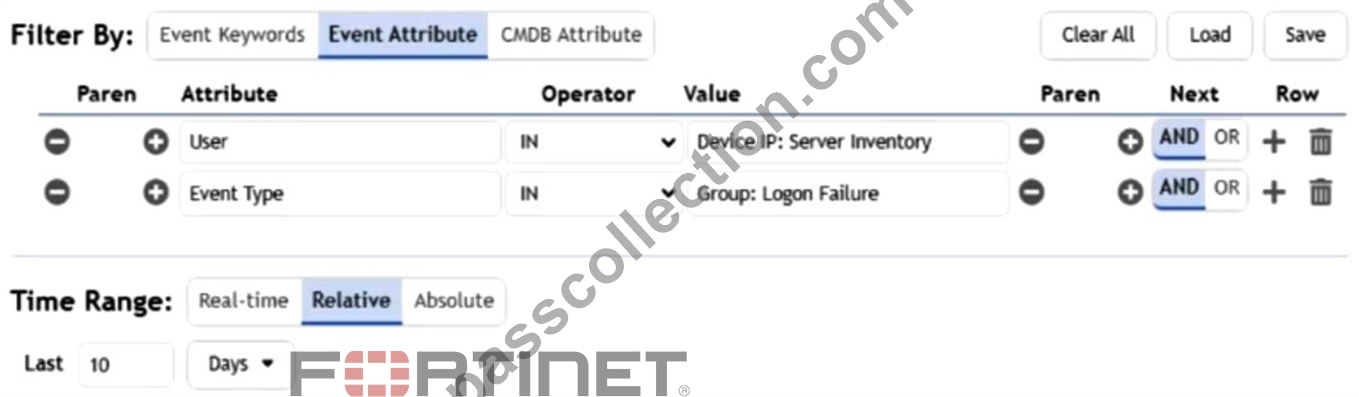
- A. You did not use the configuration management database (CMDB) group search properly.
- B. You must set the Operator to = for both queries.
- C. There is a nested query attribute type mismatch.
- D. You must set the Time Range to Real-time to identify login failures.
- E. You cannot reference both the User and Event Type attributes in the same analytics search.
Answer: C
Explanation:
The query contains a nested query attribute type mismatch because the User attribute is being compared against a Device IP group value. The attribute type and referenced group type must match for the search to return results.
NEW QUESTION # 37
......
NSE6_FSM_AN-7.4 Questions - Truly Beneficial For Your Fortinet Exam: https://www.passcollection.com/NSE6_FSM_AN-7.4_real-exams.html
