

May-2026 Free Palo Alto Networks CloudSec-Pro Exam Question Practice Exams
Ace CloudSec-Pro Certification with 260 Actual Questions
Palo Alto Networks CloudSec-Pro Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 135
Which container image scan is constructed correctly?
- A. twistcli images scan --address https://us-west1.cloud.twistlock.com/us-3-123456789 --container myimage/ latest --details
- B. twistcli images scan --address https://us-west1.cloud.twistlock.com/us-3-123456789 --container myimage/ latest
- C. twistcli images scan --docker-address https://us-west1.cloud.twistlock.com/us-3-123456789 myimage/ latest
- D. twistcli images scan --address https://us-west1.cloud.twistlock.com/us-3-123456789 myimage/latest
Answer: D
Explanation:
The correct construction for scanning a container image using the TwistCLI tool in Prisma Cloud is option B.
This command specifies the address of the Prisma Cloud Console and the image to be scanned, including its tag. The TwistCLI tool is part of Prisma Cloud's capabilities to integrate security into the CI/CD pipeline, allowing for the scanning of images for vulnerabilities as part of the build process, thus ensuring that only secure images are deployed.
NEW QUESTION # 136
A customer has a large environment that needs to upgrade Console without upgrading all Defenders at one time.
What are two prerequisites prior to performing a rolling upgrade of Defenders? (Choose two.)
- A. a second location where you can install the Console
- B. all Defenders set in read-only mode before execution of the rolling upgrade
- C. an existing Console at version n-1
- D. manual installation of the latest twistcli tool prior to the rolling upgrade
- E. additional workload licenses are required to perform the rolling upgrade
Answer: C,D
Explanation:
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin-compute/upgrade
/upgrade_process_saas After the Console has been upgraded, check and upgrade any of the Defenders that have reached the end of their support lifecycle (Defenders are backward compatible for N-2 releases). The Defender release image is built from the UBI8-minimal base image and on upgrade it is a full container image upgrade, which means that the old Defender container is replaced with a new container. Then, upgrade all other Prisma Cloud components, such as the Jenkins plugin.
NEW QUESTION # 137
Which ROL query is used to detect certain high-risk activities executed by a root user in AWS?
- A. event from cloud.audit_logs where Risk.Level = 'high' AND user = 'root'
- B. event from cloud.security_logs where operation IN ( 'ChangePassword', 'ConsoleLogin',
'DeactivateMFADevice', 'DeleteAccessKey' , 'DeleteAlarms' ) AND user = 'root' - C. event from cloud.audit_logs where operation IN ( 'ChangePassword', 'ConsoleLogin',
'DeactivateMFADevice', 'DeleteAccessKey' , 'DeleteAlarms' ) AND user = 'root' - D. config from cloud.audit_logs where operation IN ( 'ChangePassword', 'ConsoleLogin',
'DeactivateMFADevice', 'DeleteAccessKey', 'DeleteAlarms' ) AND user = 'root'
Answer: C
Explanation:
https://docs.prismacloud.io/en/classic/rql-reference/rql-reference/event-query/event-query-examples
https://docs.prismacloud.io/en/classic/rql-reference/rql-reference/event-query/event-query- examples#idda895fd2-4496-4b31-9766-7d50215dcc18
NEW QUESTION # 138
A customer has Defenders connected to Prisma Cloud Enterprise. The Defenders are deployed as a DaemonSet in OpenShift.
How should the administrator get a report of vulnerabilities on hosts?
- A. Navigate to Monitor > Vulnerabilities > CVE Viewer
- B. Navigate to Defend > Vulnerabilities > VM Images
- C. Navigate to Monitor > Vulnerabilities > Hosts
- D. Navigate to Defend > Vulnerabilities > Hosts
Answer: C
Explanation:
To view the vulnerabilities identified on a host, navigating to the "Monitor > Vulnerabilities > Hosts" section within the Prisma Cloud Console is the correct approach. This section is specifically designed to provide a comprehensive overview of all detected vulnerabilities within the host environment, offering detailed insights into each vulnerability's nature, severity, and potential impact.
This pathway allows users to efficiently assess the security posture of their hosts, prioritize vulnerabilities based on their severity, and take appropriate remediation actions. The "Hosts" section under "Vulnerabilities" is tailored to display vulnerabilities related to host configurations, installed software, and other host-level security concerns, making it the ideal location within the Prisma Cloud Console for this purpose.
NEW QUESTION # 139
Which two bot types are part of Web Application and API Security (WAAS) bot protection? (Choose two.)
- A. Chat bots
- B. Unknown bots
- C. User-defined bots
- D. Customer bots
Answer: B,C
Explanation:
Web Application and API Security (WAAS) bot protection within the Prisma Cloud ecosystem includes various types of bots, with "User-defined bots" and "Unknown bots" being two key categories. User-defined bots refer to bots that organizations have explicitly identified and categorized based on their behavior and purpose. These can include legitimate bots such as search engine crawlers or internal automation tools, which are recognized and allowed based on predefined criteria set by the user.
Unknown bots, on the other hand, encompass bots that have not been explicitly identified or categorized by the user or the system. These can potentially include malicious bots that attempt to scrape data, perform DDoS attacks, or exploit vulnerabilities in web applications and APIs. The categorization of unknown bots is crucial for maintaining security, as it allows for the monitoring and analysis of bot behavior to identify potential threats and take appropriate actions.
In the context of Prisma Cloud and its emphasis on securing cloud-native applications, the differentiation between user-defined and unknown bots is significant. Prisma Cloud's approach to WAAS bot protection is designed to provide granular control over bot traffic, enabling organizations to distinguish between beneficial and harmful bot activities. This aligns with the broader goal of ensuring the security and integrity of web applications and APIs in a cloud environment, as highlighted in documents such as the "Prisma-Cloud- Visibility-and-Control-Qualification-Guide" and "Guide-to-CSPM-Tools-Email-Social -LP-Copy." These resources emphasize the importance of comprehensive security measures that include the management of bot traffic to protect against a wide range of web-based threats.
References:
"Prisma-Cloud-Visibility-and-Control-Qualification-Guide" discusses the importance of visibility and control in cloud environments, including the management of bot traffic as part of a comprehensive security strategy.
"Guide-to-CSPM-Tools-Email-Social -LP-Copy" highlights the need for advanced security tools and practices, such as WAAS bot protection, to manage and mitigate the risks associated with web applications and APIs in the cloud.
NEW QUESTION # 140
When would a policy apply if the policy is set under Defend > Vulnerability > Images > Deployed?
- A. when a serverless repository is scanned
- B. when the Image is built
- C. when a Container is started form an Image
- D. when the Image is built and when a Container is started form an Image
Answer: C
Explanation:
In Prisma Cloud, policies set under "Defend > Vulnerability > Images > Deployed" are specifically designed to apply at runtime, i.e., when a container is instantiated from an image. This ensures that any image, regardless of its point of origin or creation time, is evaluated against the defined vulnerability policies at the time it is deployed as a container in the environment. This runtime enforcement is crucial for catching vulnerabilities that may not have been present or detected during the image build phase, providing an additional layer of security for running applications.
https://docs.paloaltonetworks.com/prisma/prisma-cloud/22-12/prisma-cloud-compute-edition-admin
/vulnerability_management/vuln_management_rules
NEW QUESTION # 141
The security auditors need to ensure that given compliance checks are being run on the host. Which option is a valid host compliance policy?
- A. Ensure host devices are not directly exposed to containers.
- B. Ensure images are created with a non-root user.
- C. Ensure compliant Docker daemon configuration.
- D. Ensure functions are not overly permissive.
Answer: C
Explanation:
The question focuses on valid host compliance policies within a cloud environment. Among the given options, the most relevant to host compliance is ensuring compliant Docker daemon configuration. Docker daemon configurations are critical for securing the host environment where containers are run. A compliant Docker daemon configuration involves setting security-related options to ensure the Docker engine operates securely. This can include configurations related to TLS for secure communication, logging levels, authorization plugins, and user namespace remapping for isolation.
Ensuring functions are not overly permissive (Option A) and ensuring images are created with a non-root user (Option C) are more directly related to the security best practices for serverless functions and container images, respectively, rather than host-specific compliance checks. Ensuring host devices are not directly exposed to containers (Option B) is also important for security, but it falls under the broader category of container runtime security rather than host-specific compliance.
Thus, the most valid host compliance policy from the given options is to ensure a compliant Docker daemon configuration, as it directly impacts the security posture of the host environment in a containerized infrastructure. This aligns with best practices for securing Docker environments and is a common recommendation in container security guidelines, including those from Docker and cybersecurity frameworks.
References:
Docker Documentation: Security configuration and best practices for Docker engine: https://docs.docker.com
/engine/security/
CIS Docker Benchmark: Providing consensus-based best practices for securing Docker environments:
https://www.cisecurity.org/benchmark/docker/
NEW QUESTION # 142
Which intensity setting for anomaly alerts is used for the measurement of 100 events over 30 days?
- A. Medium
- B. Very High
- C. Low
- D. High
Answer: A
Explanation:
In the context of setting anomaly alert intensities in Prisma Cloud, an intensity setting of "Medium" could be used for the measurement of 100 events over 30 days. This setting indicates a moderate level of anomaly detection sensitivity, which is suitable for environments where there is a need to balance between detecting potential security issues and minimizing false positives.
Reference: https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin/manage-prisma- cloud- administrators/define-prisma-cloud-enterprise-settings.html
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin/manage-prisma-cloud- administrators/define-prisma-cloud-enterprise-settings
NEW QUESTION # 143
Which three fields are mandatory when authenticating the Prisma Cloud plugin in the IntelliJ application?
(Choose three.)
- A. Access Key
- B. Tags
- C. Asset Name
- D. Secret Key
- E. Prisma Cloud API URL
Answer: A,D,E
Explanation:
Reference: https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin/prisma-cloud-devops- security/use-the-prisma-cloud-plugin-for-intellij.html When authenticating the Prisma Cloud plugin in the IntelliJ application, the mandatory fields are the Secret Key, Prisma Cloud API URL, and Access Key. These credentials are required to securely authenticate and enable the plugin to communicate with the Prisma Cloud API, ensuring that the plugin can perform its intended functions within the development environment.
NEW QUESTION # 144
Which two statements explain differences between build and run config policies? (Choose two.)
- A. Run policies monitor resources and check for potential issues after these cloud resources are deployed.
- B. Run policies monitor network activities in the environment and check for potential issues during runtime.
- C. Run and Network policies belong to the configuration policy set.
- D. Build policies allow checking for security misconfigurations in the IaC templates and ensure these issues do not get into production.
Answer: A,D
Explanation:
The Run policies monitor resources and check for potential issues once these cloud resources are deployed Build policies enable you to check for security misconfigurations in the IaC templates and ensure that these issues do not make their way into production. https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma- cloud-admin/prisma-cloud-policies/create-a-policy
* B. Build policies: These are designed to identify insecure configurations in your Infrastructure as Code (IaC) templates, such as AWS CloudFormation, HashiCorp Terraform, and Kubernetes App manifests.
The goal of build policies is to detect security issues early in the development process, before the actual resources are deployed in runtime environments. This helps ensure that security issues are identified and remediated before they can affect production1.
* D. Run policies: These policies are focused on monitoring the deployed cloud resources and checking for potential issues during their operation. Run policies are essential for ongoing security and compliance in the production environment, as they provide visibility into the actual state of resources and their activities1.
Run and Network policies (A) are indeed part of the configuration policy set, but they do not highlight the difference between build and run policies. Similarly, while Run policies do monitor network activities , this statement does not contrast them with Build policies.
NEW QUESTION # 145
Which Defender type performs registry scanning?
- A. RASP
- B. Serverless
- C. Container
- D. Host
Answer: C
Explanation:
In Prisma Cloud, the Defender type responsible for performing registry scanning is the Container Defender.
Registry scanning is crucial for ensuring that container images stored in registries are free from vulnerabilities and compliance issues before they are deployed. Container Defenders scan images within container registries, identifying security risks and ensuring that only secure container images are used in deployment, thereby maintaining the integrity and security of containerized applications.
NEW QUESTION # 146
An administrator has been tasked with creating a custom service that will download any existing compliance report from a Prisma Cloud Enterprise tenant.
In which order will the APIs be executed for this service?
(Drag the steps into the correct order of occurrence, from the first step to the last.)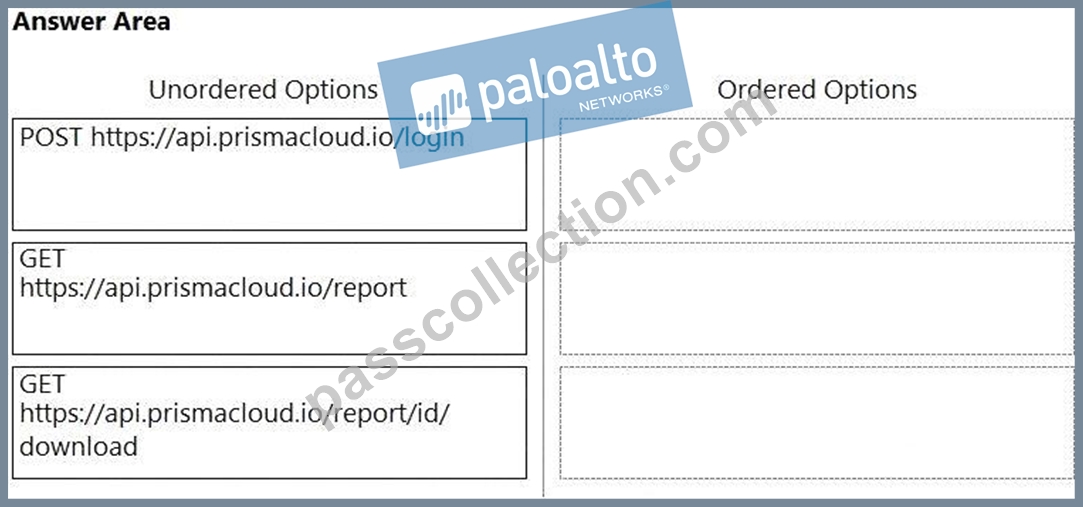
Answer:
Explanation: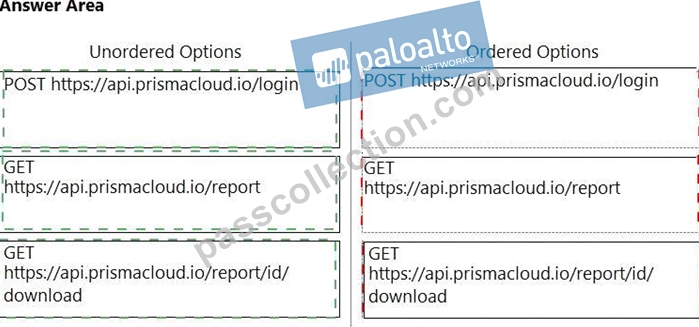
Explanation:
1. Post /Login 2. Get /report 3. Get report/id/download
NEW QUESTION # 147
Put the steps of integrating Okta with Prisma Cloud in the right order in relation to CIEM or SSO okra integration.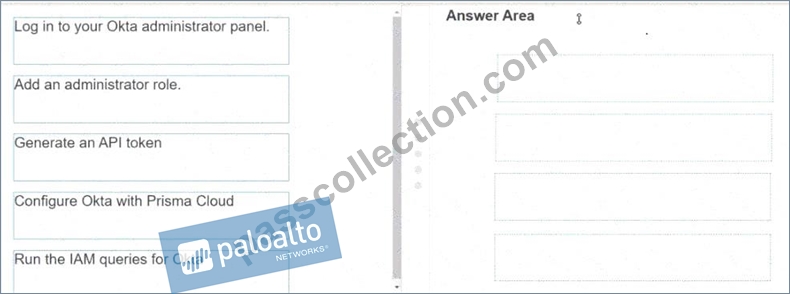
Answer:
Explanation: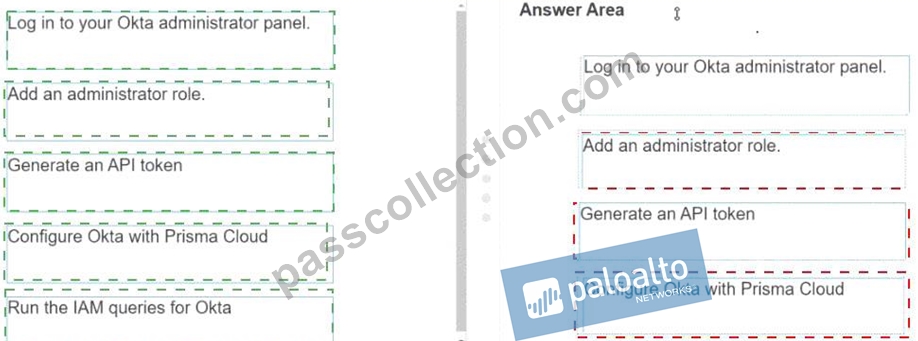
Explanation:
* Log in to your Okta administrator panel.
* Add an administrator role.
* Generate an API token.
* Configure Okta with Prisma Cloud.
* Run the IAM queries for Okta.
When integrating Okta with Prisma Cloud, especially in the context of Cloud Infrastructure Entitlement Management (CIEM) or Single Sign-On (SSO) integration, the process must be conducted in a sequence that establishes the necessary permissions and configurations for successful integration.
The first step is to log in to the Okta administrator panel. This is where you will manage your Okta settings and begin the integration process.
Once logged in, the next step is to add an administrator role. This involves assigning a role within Okta that has the appropriate permissions to create and manage API tokens and to perform integration tasks.
After setting up the correct administrative role, the third step is to generate an API token. This token will be used to authenticate the communications between Okta and Prisma Cloud. The API token acts as a secure method of verifying that requests made to Prisma Cloud are authorized.
With the API token generated, the fourth step is to configure Okta with Prisma Cloud. This step typically involves entering the API token into Prisma Cloud and setting up the necessary configurations within Prisma Cloud to recognize and accept authentication requests from Okta.
The final step is to run the Identity and Access Management (IAM) queries for Okta within Prisma Cloud.
This step is crucial for CIEM, as it allows Prisma Cloud to query Okta for identity information, user roles, and entitlements, ensuring that the correct permissions are enforced across the cloud environment and that SSO is functioning correctly.
Following these steps in order will ensure that Okta is properly integrated with Prisma Cloud, providing a secure and efficient method for managing cloud access and entitlements.
NEW QUESTION # 148
A customer has a requirement to scan serverless functions for vulnerabilities.
Which three settings are required to configure serverless scanning? (Choose three.)
- A. Region
- B. Provider
- C. Defender Name
- D. Credential
- E. Console Address
Answer: A,B,D
Explanation:
To configure serverless scanning in a cloud security platform like Prisma Cloud, the system needs to know where (Region) the serverless functions are deployed, how to access them (Credential), and on which cloud platform they are running (Provider). These settings ensure that the scanning tool can accurately locate and authenticate to the serverless functions across different cloud environments for vulnerability assessment. This aligns with the principle of providing comprehensive visibility and consistent security across multi-cloud environments as outlined in the "Guide to Cloud Security Posture Management Tools" document.
Reference: https://docs.paloaltonetworks.com/prisma/prisma-cloud/21-04/prisma-cloud-compute-edition- admin/vulnerability_management/serverless_functions.html
NEW QUESTION # 149
Which two attributes are required for a custom config RQL? (Choose two.)
- A. cloud.account
- B. api.name
- C. tag
- D. json.rule
Answer: B,D
Explanation:
For a custom config Resource Query Language (RQL) in Prisma Cloud, two essential attributes are "json.
rule" and "api.name." The "json.rule" attribute allows users to specify the JSON structure that defines the criteria or conditions of the query, essentially dictating what the query is looking for within the cloud environment. The "api.name" attribute identifies the specific API endpoint that the query will target, providing context and scope for the query. Together, these attributes enable users to craft precise and targeted queries that can assess the configuration and security posture of cloud resources, aiding in compliance checks, security assessments, and other governance tasks.
NEW QUESTION # 150
What will happen when a Prisma Cloud Administrator has configured agentless scanning in an environment that also has Host and Container Defenders deployed?
- A. Both agentless and Defender scans will be disabled and an error message will be received.
- B. Defender scans will automatically be disabled, so agentless scans are the only scans occurring.
- C. Agentless scan will automatically be disabled, so Defender scans are the only scans occurring.
- D. Agentless scans do not conflict with Defender scans, so both will run.
Answer: D
Explanation:
In a Prisma Cloud environment where both agentless scanning and Defender-based scans (Host and Container Defenders) are configured, there is no inherent conflict between these two scanning methods. Both agentless scans and Defender scans are designed to complement each other, providing comprehensive coverage and depth in the security analysis of the environment. Agentless scans offer a broad, less intrusive overview, while Defender scans provide deep, detailed insights into the security posture. Therefore, both types of scans will run concurrently, enhancing the overall security visibility and protection of the environment without disabling or interfering with each other's operations.
The agentless scanning architecture lets you inspect a host and the container images in that host without having to install an agent or affecting its execution. https://docs.paloaltonetworks.com/prisma/prisma-cloud
/prisma-cloud-admin-compute/agentless-scanning/onboard-accounts
NEW QUESTION # 151
Given a default deployment of Console, a customer needs to identify the alerted compliance checks that are set by default.
Where should the customer navigate in Console?
- A. Manage > Compliance
- B. Custom > Compliance
- C. Defend > Compliance
- D. Monitor > Compliance
Answer: C
Explanation:
Reference: https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin-compute/compliance/ manage_compliance.html In the context of Prisma Cloud by Palo Alto Networks, the correct navigation to identify alerted compliance checks set by default is under the "Defend" section, specifically at "Defend > Compliance." This section is designed to allow users to configure and manage compliance policies and rules, monitor compliance statuses, and review alerts related to compliance violations. The "Defend" section is tailored for setting up defenses, including compliance standards, against potential security risks within the cloud environment, making it the logical location for managing and reviewing compliance-related alerts and settings.
NEW QUESTION # 152
Which three actions are available for the container image scanning compliance rule? (Choose three.)
- A. Snooze
- B. Block
- C. Alert
- D. Ignore
- E. Allow
Answer: B,C,D
Explanation:
The Prisma Cloud documentation specifies the actions that can be taken for container image scanning compliance rules as:
* C. Block: This action prevents the use of a container image if it fails to meet the defined compliance criteria.
* D. Ignore: This action allows the image to bypass the compliance check, effectively overlooking the identified issues.
* E. Alert: This action triggers an alert to notify the relevant stakeholders about the compliance status of the container image.
These actions are integral to Prisma Cloud's governance capabilities, allowing organizations to enforce their security and compliance policies effectively. By setting up these rules, teams can ensure that only images that comply with their standards are deployed, while also having the flexibility to ignore certain images or receive alerts for further investigation.
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin-compute/compliance
/trusted_images
NEW QUESTION # 153
......
CloudSec-Pro Questions PDF [2026] Use Valid New dump to Clear Exam: https://www.passcollection.com/CloudSec-Pro_real-exams.html
PASS Palo Alto Networks CloudSec-Pro EXAM WITH UPDATED DUMPS: https://drive.google.com/open?id=1DJuDKpfGv64tPOpMVFOX5n6B7KvgMQcP
